Citrix Confirms Two NetScaler RCE Zero-Days Exploited in the Wild
Citrix says exploits of CVE-2026-88771 and CVE-2026-88772 have been observed on unmitigated NetScaler ADC and Gateway deployments, and CISA added both flaws to the KEV catalog on September 27, 2026.
Noah Park, ResponseNew York2 min read
NEW YORK - Citrix confirmed on September 27, 2026, that two critical NetScaler remote code execution flaws, CVE-2026-88771 and CVE-2026-88772, have been exploited on unmitigated deployments, and the U.S. Cybersecurity and Infrastructure Security Agency added both to its Known Exploited Vulnerabilities catalog the same day.
Security bulletin CTX697096 covers customer-managed NetScaler ADC and NetScaler Gateway. Citrix describes CVE-2026-88771 as improper input validation that can let an unauthenticated attacker execute arbitrary commands. The listed precondition is every NetScaler ADC and NetScaler Gateway deployment, including the default configuration, with no extra feature required. CVE-2026-88772 is a memory overflow that can lead to remote code execution or denial of service when DTLS is enabled, and Citrix notes that DTLS is on by default for VPN virtual servers. Both are scored CVSS 9.5 in Citrix's v4.0 ratings, as reported by BleepingComputer and watchTowr. The same bulletin fixes six additional NetScaler flaws, eight in all. It applies to customer-managed appliances. BleepingComputer reported that Cloud Software Group is upgrading Citrix-managed cloud services and Citrix-managed Adaptive Authentication.
Affected builds are NetScaler ADC and Gateway 14.1 before 14.1-73.37, 13.1 before 13.1-64.23, NetScaler ADC 14.1-FIPS before 14.1-73.37 FIPS, and NetScaler ADC 13.1-FIPS and 13.1-NDcPP before 13.1-37.279. Secure Private Access hybrid deployments that use NetScaler instances are also affected. Fixed builds are 14.1-73.37 and later, 13.1-64.23 and later releases of 13.1, 14.1-73.37 FIPS and later, and 13.1-37.279 and later. watchTowr says Citrix has not published a workaround, so the upgrade is the fix. On the 13.1 train, watchTowr says to run show ns variable first and, if any variables are returned, install 13.1-64.24 instead, to avoid a known reboot loop during the upgrade.
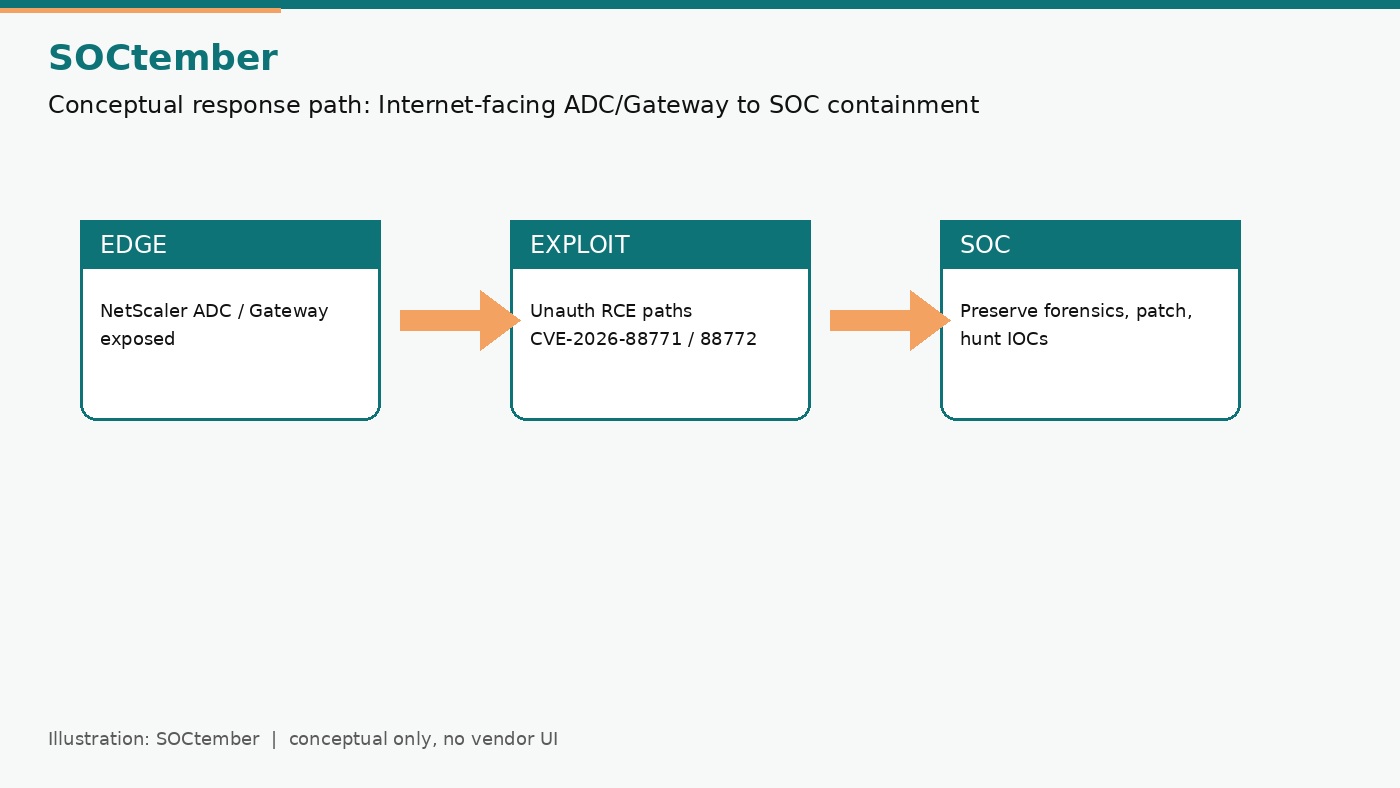
CISA said it has received reports and partner threat intelligence that threat actors are actively exploiting the vulnerabilities globally, and that each flaw can independently enable remote code execution. CISA urged administrators to review Citrix's advisories and, if possible, to check for compromise before patching. If compromise is suspected, CISA said to preserve forensic evidence before applying updates, because updates may remove forensic visibility. Citrix has published indicators of compromise through NetScaler Console. watchTowr says those indicators do not cover every technique, so a clean scan is not proof that an appliance was not compromised. watchTowr had warned publicly on September 26, 2026, before the CVE identifiers existed, that multiple unpatched NetScaler remote code execution flaws were being exploited and that the information was credible and came from forensic investigations. BleepingComputer reported that the NCSC said exploitation had been identified at multiple Citrix customers worldwide and that the agency did not know whether the attacks were widespread.
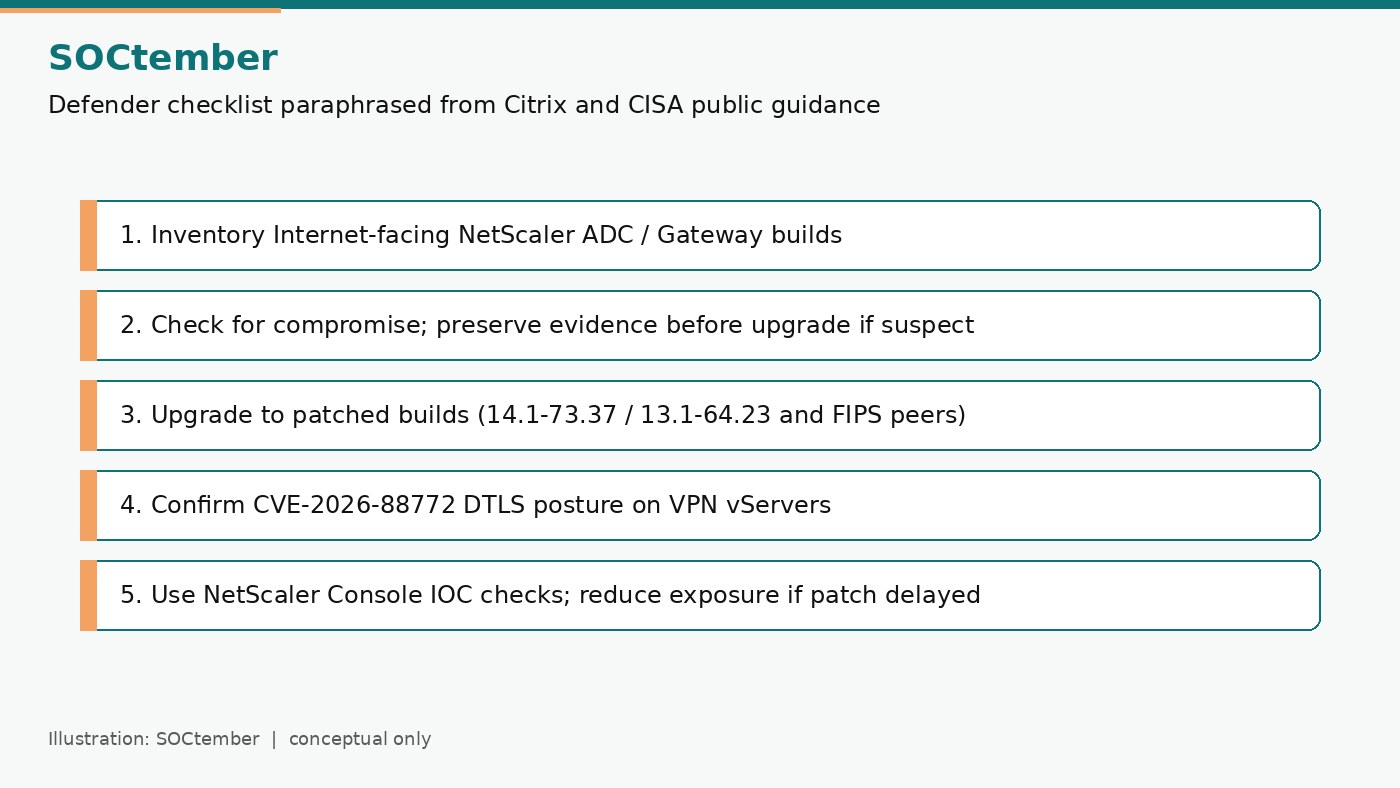
For security operations teams, an internet-facing NetScaler ADC or Gateway is a containment and forensics case, not only a version ticket. watchTowr's order of work is to capture logs, a snapshot, a support bundle, and a core dump from each exposed appliance, check for compromise, then install the fixed build. After the upgrade, rotate passwords, secrets, and certificates stored on or used through the appliance, forward NetScaler logs to the SIEM, and keep management interfaces off the public internet. Prioritize Gateway, VPN, and AAA virtual servers that are reachable from untrusted networks, and confirm the DTLS setting on VPN virtual servers for CVE-2026-88772.
Sources:
Noah Park covers incident response and blue-team operations for SOCtember from New York.
Related stories
Response
F5 Warns of Exploited BIG-IP APM Flaw Enabling Unauthenticated Remote Code Execution
Response
Check Point Patches Actively Exploited Management Server Path Traversal
Response
CISA Flags TeamCity Flaw CVE-2026-63077 as Used in Ransomware Campaigns
Threat Intel