Response, New York. Noah Park: Check Point Patches Actively Exploited Management Server Path Traversal. Detection, Dallas. Ava Okello: Report Finds Nearly Half of Deployed Detections Need Attention Before SOCs Can Trust Them.
RESPONSEHuntress Reconstructs Akira Ransomware Attack From Registry Artifacts After Post-Compromise EDR InstallNEW YORKNoah ParkDETECTIONCrowdStrike Shows Attackers Bypass LLM Safety Classifiers by Splitting Harmful Goals Into Benign SubtasksLONDONAva OkelloTOOLSUnit 42 Tracks ChainDrop and PolinRider Stealing Cloud Build Credentials Through Blockchain C2 Dead DropsAUSTINJames WhitfordTHREAT INTELCisco Talos Tracks UAT-11985 Phishing Taiwan Researchers With AI-Assisted Invites and Real-Time Google Login RelaysSINGAPOREPriya ShahRESPONSEHuntress Sees Active Exploitation of AhsayCBS Backup Flaws Dropping Webshells and XMRig Across Five OrganizationsNEW YORKNoah ParkDETECTIONMalware Now Embeds Instructions Meant to Steer AI Analysis Tools, Cisco Talos Finds Across 84 SamplesLONDONAva OkelloTHREAT INTELRussia-Aligned Spies Retool MATCHBOIL Malware and Widen Attacks to Ukrainian Transport, Manufacturing and Energy FirmsSINGAPOREPriya ShahRESPONSEFBI and Secret Service Warn FortiBleed Hackers Are Locking Some Fortinet Customers Out of Their Own FirewallsNEW YORKNoah ParkDETECTIONAttackers Are Testing Stolen AWS Keys for Amazon Bedrock Access, Leaving a Pattern Defenders Can SpotLONDONAva OkelloRESPONSEPoisoned Tensorlake npm Release Hid a Worm That Deletes Home Directories if Victims Revoke the Stolen TokenNEW YORKNoah ParkTHREAT INTELFBI Seizes Integrity Tech Hacking Tools as Allies Detail How China-Linked Hackers Steal Government EmailSINGAPOREPriya ShahDETECTIONMalware That Reads Its Orders From a Poem on GitHub Has Hit More Than 3,400 Exposed AI and Developer ServersLONDONAva OkelloTHREAT INTELIran-Linked Hackers Posing as Dubai Airports Recruiters Hide Malware in a Visual Studio Coding TestSINGAPOREPriya ShahTHREAT INTELFake ChatGPT and Gemini Ad Portals Use Browser-in-the-Browser Pop-Ups to Steal Logins and MFA CodesSINGAPOREPriya ShahDETECTIONMicrosoft Warns ClickFix Lures Now Hide Their Payload in the Browser CacheLONDONAva OkelloTHREAT INTELClingSTUN Backdoor Turns Unpatched IoT Devices Into Proxies Hidden in Public STUN TrafficSINGAPOREPriya ShahDETECTIONThales SConnect Flaw Opened Drive-By Code Execution on PCs Used for SWIFT 3SKey Sign-InLONDONAva OkelloRESPONSECitrix Patches NetScaler SAML Zero-Day CVE-2026-88779 After Attacks Reboot Freshly Patched AppliancesNEW YORKNoah ParkTHREAT INTELRapid7 Tracks BPFDoor and AVERAT Implants Mimicking Asian Mail GatewaysSINGAPOREPriya ShahRESPONSEMicrosoft Tracks Unauthenticated Zimbra SNMP Command Injection Exploited as CVE-2026-73570NEW YORKNoah ParkOPINIONSOC Autonomy Without Governance Recreates the Same Failure Modes AI Was Meant to FixLONDONElena VosTHREAT INTELMandiant Warns ShinyHunters Bypass WAFs to Resume PeopleSoft Mass ExploitationSINGAPOREPriya ShahDETECTIONMicrosoft Tracks EvilTokens Phishing Kit Behind Device Code Token TheftLONDONAva OkelloRESPONSECitrix Confirms Two NetScaler RCE Zero-Days Exploited in the WildNEW YORKNoah ParkDETECTIONHuntress Finds Threat Actor Compiling Silent XMR Miner Directly on EndpointLONDONAva OkelloRESPONSECISA Puts MikroTik RouterOS SSH Workflow Flaw CVE-2026-67279 on KEVWASHINGTONNoah ParkRESPONSECheck Point Patches Actively Exploited Management Server Path TraversalNEW YORKNoah ParkDETECTIONReport Finds Nearly Half of Deployed Detections Need Attention Before SOCs Can Trust ThemDALLASAva OkelloRESPONSEHuntress Reconstructs Akira Ransomware Attack From Registry Artifacts After Post-Compromise EDR InstallNEW YORKNoah ParkDETECTIONCrowdStrike Shows Attackers Bypass LLM Safety Classifiers by Splitting Harmful Goals Into Benign SubtasksLONDONAva OkelloTOOLSUnit 42 Tracks ChainDrop and PolinRider Stealing Cloud Build Credentials Through Blockchain C2 Dead DropsAUSTINJames WhitfordTHREAT INTELCisco Talos Tracks UAT-11985 Phishing Taiwan Researchers With AI-Assisted Invites and Real-Time Google Login RelaysSINGAPOREPriya ShahRESPONSEHuntress Sees Active Exploitation of AhsayCBS Backup Flaws Dropping Webshells and XMRig Across Five OrganizationsNEW YORKNoah ParkDETECTIONMalware Now Embeds Instructions Meant to Steer AI Analysis Tools, Cisco Talos Finds Across 84 SamplesLONDONAva OkelloTHREAT INTELRussia-Aligned Spies Retool MATCHBOIL Malware and Widen Attacks to Ukrainian Transport, Manufacturing and Energy FirmsSINGAPOREPriya ShahRESPONSEFBI and Secret Service Warn FortiBleed Hackers Are Locking Some Fortinet Customers Out of Their Own FirewallsNEW YORKNoah ParkDETECTIONAttackers Are Testing Stolen AWS Keys for Amazon Bedrock Access, Leaving a Pattern Defenders Can SpotLONDONAva OkelloRESPONSEPoisoned Tensorlake npm Release Hid a Worm That Deletes Home Directories if Victims Revoke the Stolen TokenNEW YORKNoah ParkTHREAT INTELFBI Seizes Integrity Tech Hacking Tools as Allies Detail How China-Linked Hackers Steal Government EmailSINGAPOREPriya ShahDETECTIONMalware That Reads Its Orders From a Poem on GitHub Has Hit More Than 3,400 Exposed AI and Developer ServersLONDONAva OkelloTHREAT INTELIran-Linked Hackers Posing as Dubai Airports Recruiters Hide Malware in a Visual Studio Coding TestSINGAPOREPriya ShahTHREAT INTELFake ChatGPT and Gemini Ad Portals Use Browser-in-the-Browser Pop-Ups to Steal Logins and MFA CodesSINGAPOREPriya ShahDETECTIONMicrosoft Warns ClickFix Lures Now Hide Their Payload in the Browser CacheLONDONAva OkelloTHREAT INTELClingSTUN Backdoor Turns Unpatched IoT Devices Into Proxies Hidden in Public STUN TrafficSINGAPOREPriya ShahDETECTIONThales SConnect Flaw Opened Drive-By Code Execution on PCs Used for SWIFT 3SKey Sign-InLONDONAva OkelloRESPONSECitrix Patches NetScaler SAML Zero-Day CVE-2026-88779 After Attacks Reboot Freshly Patched AppliancesNEW YORKNoah ParkTHREAT INTELRapid7 Tracks BPFDoor and AVERAT Implants Mimicking Asian Mail GatewaysSINGAPOREPriya ShahRESPONSEMicrosoft Tracks Unauthenticated Zimbra SNMP Command Injection Exploited as CVE-2026-73570NEW YORKNoah ParkOPINIONSOC Autonomy Without Governance Recreates the Same Failure Modes AI Was Meant to FixLONDONElena VosTHREAT INTELMandiant Warns ShinyHunters Bypass WAFs to Resume PeopleSoft Mass ExploitationSINGAPOREPriya ShahDETECTIONMicrosoft Tracks EvilTokens Phishing Kit Behind Device Code Token TheftLONDONAva OkelloRESPONSECitrix Confirms Two NetScaler RCE Zero-Days Exploited in the WildNEW YORKNoah ParkDETECTIONHuntress Finds Threat Actor Compiling Silent XMR Miner Directly on EndpointLONDONAva OkelloRESPONSECISA Puts MikroTik RouterOS SSH Workflow Flaw CVE-2026-67279 on KEVWASHINGTONNoah ParkRESPONSECheck Point Patches Actively Exploited Management Server Path TraversalNEW YORKNoah ParkDETECTIONReport Finds Nearly Half of Deployed Detections Need Attention Before SOCs Can Trust ThemDALLASAva Okello
Commentary from named writers on detection, response, and the tools of daily operations.
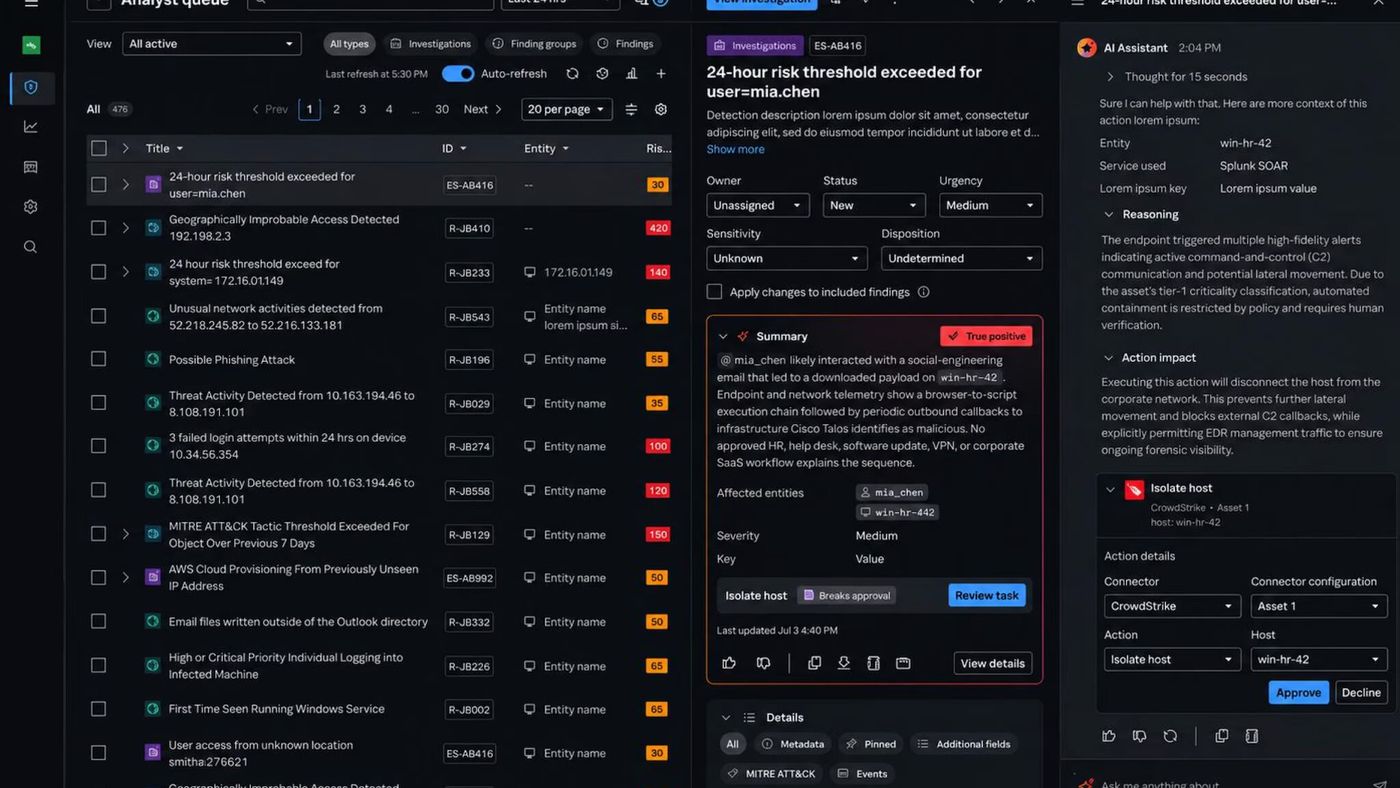
Photo: Splunk. Enterprise Security 8.7 product UI showing the AI SOC Analyst moving from investigation context to a governed response action with Approve or Decline.
Splunk Enterprise Security 8.7 frames the Agentic SOC as a move from AI-assisted investigation to governed autonomous response, where permitted actions, approval gates, evidence, policy, and auditability matter more than buying a stronger model.
LONDON - SOCs still treat missed alerts as a people problem. Detection engineering evidence says most alert fatigue is manufactured upstream in the detection pipeline. Future of SecOps (Aug 2026, Marta K.) described a review that blamed an analyst after a shift queue of more than 800 alerts, including EDR and identity duplicates of one medium-severity credential anomaly. Alert fatigue is volume, noise, duplication, and weak prioritization exceeding review capacity. Intezer (THN Sep 12, 2026): ~16.9M SOC alerts Feb-Jun 2026; ~73k AI-related (0.43%), up 685%; of AI-related, 94.1% benign tool use, 5.8% unsafe/policy, 0.02% confirmed attacks; no confirmed org-agent takeovers. ISACA 2025 via FoS: 55% understaffed; 38% need 3-6 months to fill entry-level. Fix: measure FP/duplicate/backlog/TTA by rule; tune defaults; correlate; severity contracts; rule owners; triage feedback. AI triage helps enrichment but cannot retire orphan rules.