Response, New York. Noah Park: Check Point Patches Actively Exploited Management Server Path Traversal. Detection, Dallas. Ava Okello: Report Finds Nearly Half of Deployed Detections Need Attention Before SOCs Can Trust Them.
RESPONSEHuntress Reconstructs Akira Ransomware Attack From Registry Artifacts After Post-Compromise EDR InstallNEW YORKNoah ParkDETECTIONCrowdStrike Shows Attackers Bypass LLM Safety Classifiers by Splitting Harmful Goals Into Benign SubtasksLONDONAva OkelloTOOLSUnit 42 Tracks ChainDrop and PolinRider Stealing Cloud Build Credentials Through Blockchain C2 Dead DropsAUSTINJames WhitfordTHREAT INTELCisco Talos Tracks UAT-11985 Phishing Taiwan Researchers With AI-Assisted Invites and Real-Time Google Login RelaysSINGAPOREPriya ShahRESPONSEHuntress Sees Active Exploitation of AhsayCBS Backup Flaws Dropping Webshells and XMRig Across Five OrganizationsNEW YORKNoah ParkDETECTIONMalware Now Embeds Instructions Meant to Steer AI Analysis Tools, Cisco Talos Finds Across 84 SamplesLONDONAva OkelloTHREAT INTELRussia-Aligned Spies Retool MATCHBOIL Malware and Widen Attacks to Ukrainian Transport, Manufacturing and Energy FirmsSINGAPOREPriya ShahRESPONSEFBI and Secret Service Warn FortiBleed Hackers Are Locking Some Fortinet Customers Out of Their Own FirewallsNEW YORKNoah ParkDETECTIONAttackers Are Testing Stolen AWS Keys for Amazon Bedrock Access, Leaving a Pattern Defenders Can SpotLONDONAva OkelloRESPONSEPoisoned Tensorlake npm Release Hid a Worm That Deletes Home Directories if Victims Revoke the Stolen TokenNEW YORKNoah ParkTHREAT INTELFBI Seizes Integrity Tech Hacking Tools as Allies Detail How China-Linked Hackers Steal Government EmailSINGAPOREPriya ShahDETECTIONMalware That Reads Its Orders From a Poem on GitHub Has Hit More Than 3,400 Exposed AI and Developer ServersLONDONAva OkelloTHREAT INTELIran-Linked Hackers Posing as Dubai Airports Recruiters Hide Malware in a Visual Studio Coding TestSINGAPOREPriya ShahTHREAT INTELFake ChatGPT and Gemini Ad Portals Use Browser-in-the-Browser Pop-Ups to Steal Logins and MFA CodesSINGAPOREPriya ShahDETECTIONMicrosoft Warns ClickFix Lures Now Hide Their Payload in the Browser CacheLONDONAva OkelloTHREAT INTELClingSTUN Backdoor Turns Unpatched IoT Devices Into Proxies Hidden in Public STUN TrafficSINGAPOREPriya ShahDETECTIONThales SConnect Flaw Opened Drive-By Code Execution on PCs Used for SWIFT 3SKey Sign-InLONDONAva OkelloRESPONSECitrix Patches NetScaler SAML Zero-Day CVE-2026-88779 After Attacks Reboot Freshly Patched AppliancesNEW YORKNoah ParkTHREAT INTELRapid7 Tracks BPFDoor and AVERAT Implants Mimicking Asian Mail GatewaysSINGAPOREPriya ShahRESPONSEMicrosoft Tracks Unauthenticated Zimbra SNMP Command Injection Exploited as CVE-2026-73570NEW YORKNoah ParkOPINIONSOC Autonomy Without Governance Recreates the Same Failure Modes AI Was Meant to FixLONDONElena VosTHREAT INTELMandiant Warns ShinyHunters Bypass WAFs to Resume PeopleSoft Mass ExploitationSINGAPOREPriya ShahDETECTIONMicrosoft Tracks EvilTokens Phishing Kit Behind Device Code Token TheftLONDONAva OkelloRESPONSECitrix Confirms Two NetScaler RCE Zero-Days Exploited in the WildNEW YORKNoah ParkDETECTIONHuntress Finds Threat Actor Compiling Silent XMR Miner Directly on EndpointLONDONAva OkelloRESPONSECISA Puts MikroTik RouterOS SSH Workflow Flaw CVE-2026-67279 on KEVWASHINGTONNoah ParkRESPONSECheck Point Patches Actively Exploited Management Server Path TraversalNEW YORKNoah ParkDETECTIONReport Finds Nearly Half of Deployed Detections Need Attention Before SOCs Can Trust ThemDALLASAva OkelloRESPONSEHuntress Reconstructs Akira Ransomware Attack From Registry Artifacts After Post-Compromise EDR InstallNEW YORKNoah ParkDETECTIONCrowdStrike Shows Attackers Bypass LLM Safety Classifiers by Splitting Harmful Goals Into Benign SubtasksLONDONAva OkelloTOOLSUnit 42 Tracks ChainDrop and PolinRider Stealing Cloud Build Credentials Through Blockchain C2 Dead DropsAUSTINJames WhitfordTHREAT INTELCisco Talos Tracks UAT-11985 Phishing Taiwan Researchers With AI-Assisted Invites and Real-Time Google Login RelaysSINGAPOREPriya ShahRESPONSEHuntress Sees Active Exploitation of AhsayCBS Backup Flaws Dropping Webshells and XMRig Across Five OrganizationsNEW YORKNoah ParkDETECTIONMalware Now Embeds Instructions Meant to Steer AI Analysis Tools, Cisco Talos Finds Across 84 SamplesLONDONAva OkelloTHREAT INTELRussia-Aligned Spies Retool MATCHBOIL Malware and Widen Attacks to Ukrainian Transport, Manufacturing and Energy FirmsSINGAPOREPriya ShahRESPONSEFBI and Secret Service Warn FortiBleed Hackers Are Locking Some Fortinet Customers Out of Their Own FirewallsNEW YORKNoah ParkDETECTIONAttackers Are Testing Stolen AWS Keys for Amazon Bedrock Access, Leaving a Pattern Defenders Can SpotLONDONAva OkelloRESPONSEPoisoned Tensorlake npm Release Hid a Worm That Deletes Home Directories if Victims Revoke the Stolen TokenNEW YORKNoah ParkTHREAT INTELFBI Seizes Integrity Tech Hacking Tools as Allies Detail How China-Linked Hackers Steal Government EmailSINGAPOREPriya ShahDETECTIONMalware That Reads Its Orders From a Poem on GitHub Has Hit More Than 3,400 Exposed AI and Developer ServersLONDONAva OkelloTHREAT INTELIran-Linked Hackers Posing as Dubai Airports Recruiters Hide Malware in a Visual Studio Coding TestSINGAPOREPriya ShahTHREAT INTELFake ChatGPT and Gemini Ad Portals Use Browser-in-the-Browser Pop-Ups to Steal Logins and MFA CodesSINGAPOREPriya ShahDETECTIONMicrosoft Warns ClickFix Lures Now Hide Their Payload in the Browser CacheLONDONAva OkelloTHREAT INTELClingSTUN Backdoor Turns Unpatched IoT Devices Into Proxies Hidden in Public STUN TrafficSINGAPOREPriya ShahDETECTIONThales SConnect Flaw Opened Drive-By Code Execution on PCs Used for SWIFT 3SKey Sign-InLONDONAva OkelloRESPONSECitrix Patches NetScaler SAML Zero-Day CVE-2026-88779 After Attacks Reboot Freshly Patched AppliancesNEW YORKNoah ParkTHREAT INTELRapid7 Tracks BPFDoor and AVERAT Implants Mimicking Asian Mail GatewaysSINGAPOREPriya ShahRESPONSEMicrosoft Tracks Unauthenticated Zimbra SNMP Command Injection Exploited as CVE-2026-73570NEW YORKNoah ParkOPINIONSOC Autonomy Without Governance Recreates the Same Failure Modes AI Was Meant to FixLONDONElena VosTHREAT INTELMandiant Warns ShinyHunters Bypass WAFs to Resume PeopleSoft Mass ExploitationSINGAPOREPriya ShahDETECTIONMicrosoft Tracks EvilTokens Phishing Kit Behind Device Code Token TheftLONDONAva OkelloRESPONSECitrix Confirms Two NetScaler RCE Zero-Days Exploited in the WildNEW YORKNoah ParkDETECTIONHuntress Finds Threat Actor Compiling Silent XMR Miner Directly on EndpointLONDONAva OkelloRESPONSECISA Puts MikroTik RouterOS SSH Workflow Flaw CVE-2026-67279 on KEVWASHINGTONNoah ParkRESPONSECheck Point Patches Actively Exploited Management Server Path TraversalNEW YORKNoah ParkDETECTIONReport Finds Nearly Half of Deployed Detections Need Attention Before SOCs Can Trust ThemDALLASAva Okello
Cisco Talos says the campaign reused real public event details, likely AI-assisted invitation templates, and an adversary-in-the-middle kit that relays Google authentication including MFA challenges over HTTP and WebSocket. ClamAV and Snort coverage plus IOCs are published.
Priya Shah, Threat Intel, Singapore
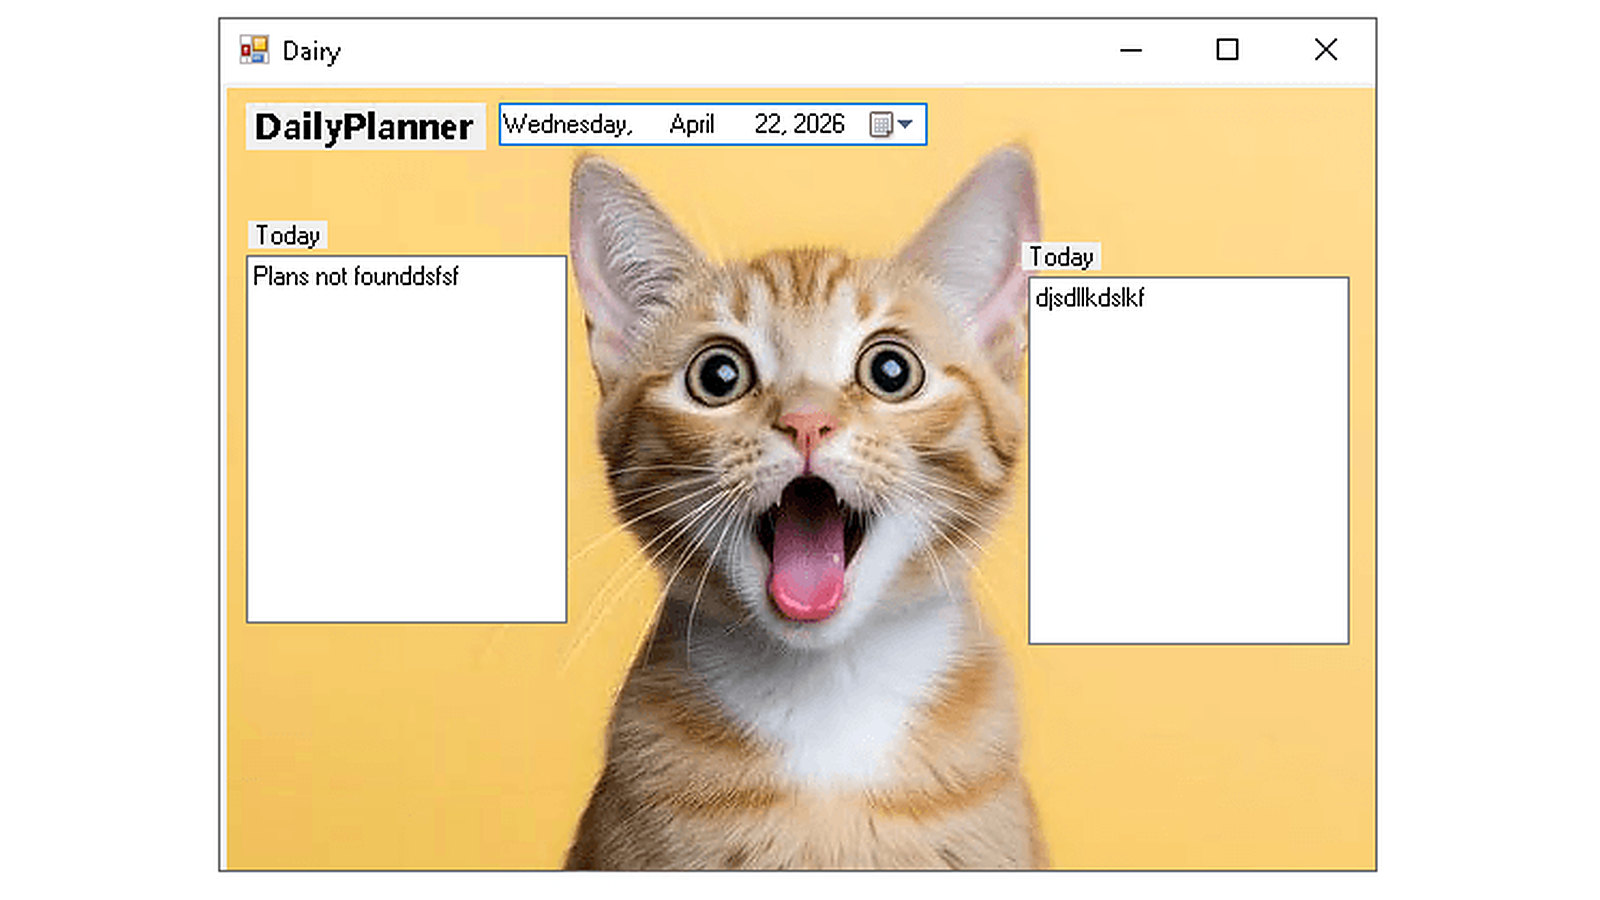
Read the storyScreenshot: ESET Research, the fake daily planner window, titled Dairy, that late 2025 MATCHBOIL samples display when opened directly, from MATCHBOIL: New tricks, same old evil intentions, Oct 8, 2026 (fair use).
ESET says UAC-0099, a group it describes as able to act as an initial access broker for Sandworm, planted its rebuilt MATCHBOIL downloader at Ukrainian transportation, manufacturing and energy companies, adding fake planner screens, sandbox checks and a new DLL variant while leaving a trail of file paths, scheduled tasks and HTTP headers defenders can hunt.
Priya Shah, Threat Intel, Singapore
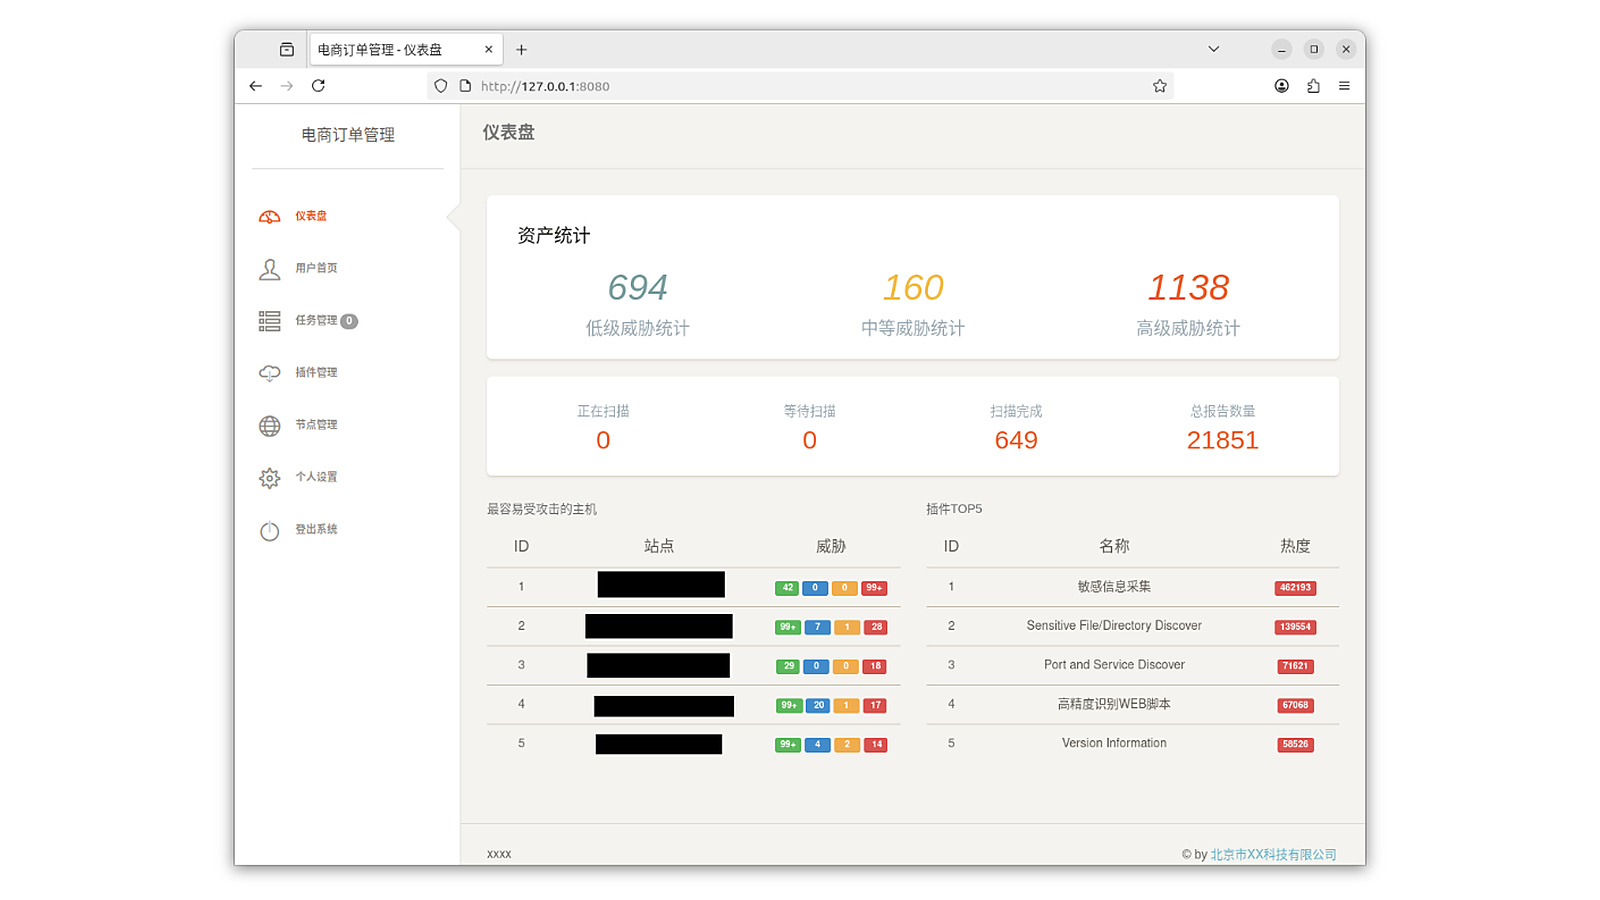
Read the storyScreenshot: FBI, via joint Cybersecurity Advisory AA26-281A, a MicroScan account dashboard showing detected vulnerabilities, recovered in FBI investigations of Integrity Technology Group, Oct 8, 2026 (fair use).
The FBI and nine partner agencies said on October 8 that hackers tied to Integrity Technology Group, a China-based company with links to the Chinese government, stole email from government, law enforcement, healthcare and religious organizations in Southeast Asia, as the Justice Department seized domains behind the company's Microscan scanner and FishHub phishing tool.
Priya Shah, Threat Intel, Singapore
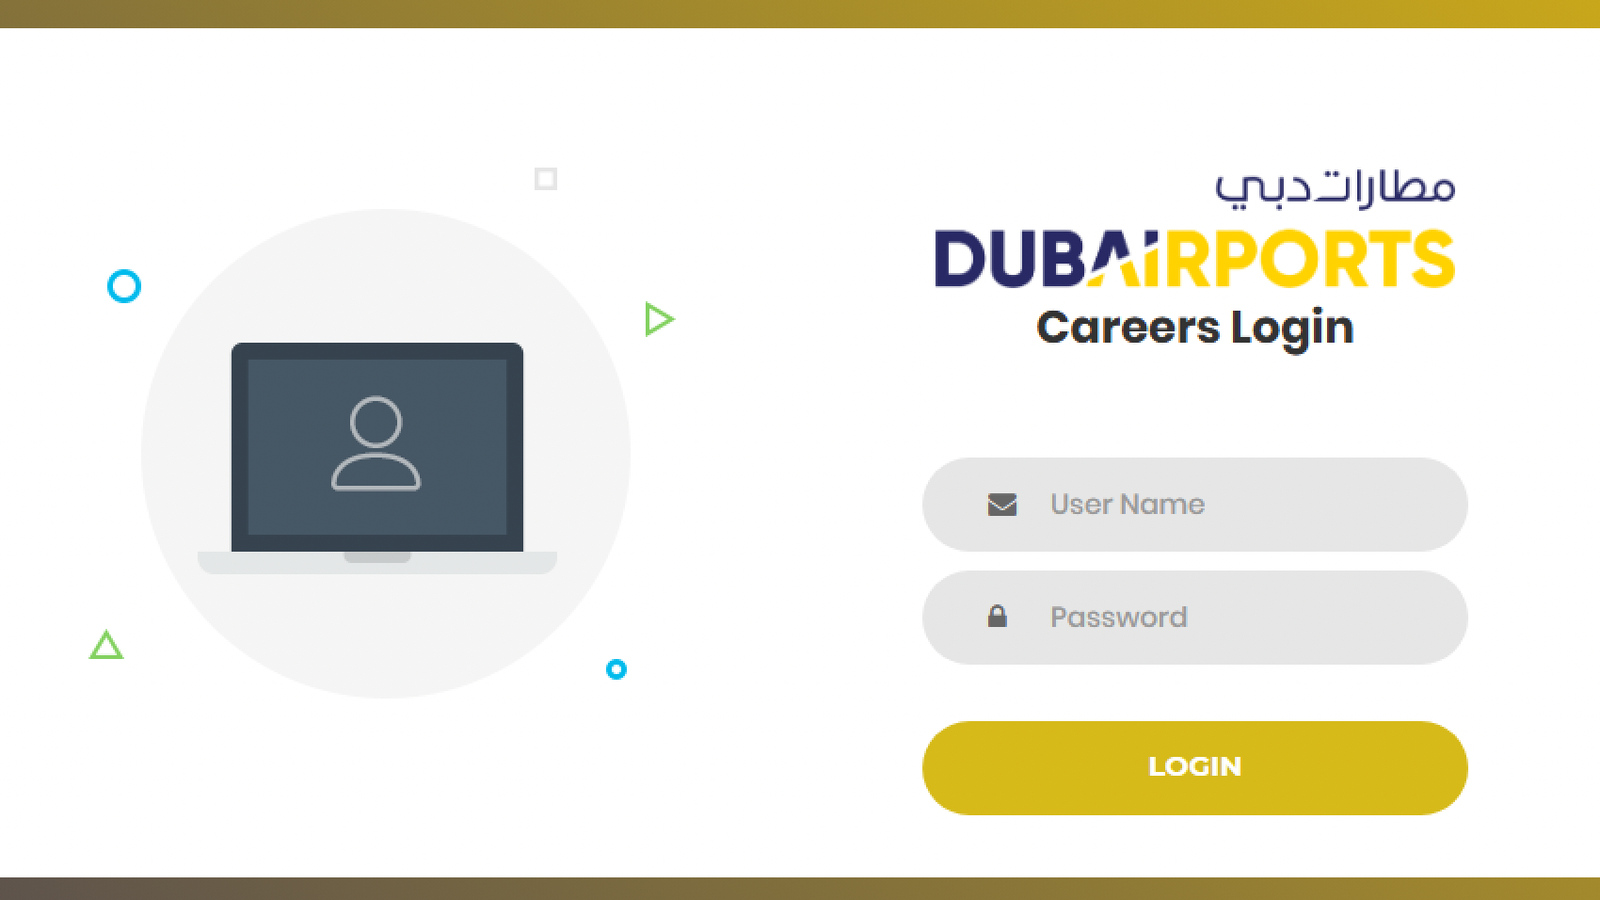
Read the storyScreenshot: Unit 42 (Palo Alto Networks), the fake Dubai Airports careers portal the attackers had the target install before sending a trojanized coding test, Oct 6, 2026 (fair use).
Unit 42 researchers said on October 6 that an Iranian state-aligned group it tracks as CL-STA-1178 sent an Iraq-based engineer a fake coding assessment that ran malware as soon as Visual Studio opened the project, then took its orders through GitHub repositories and issue comments.
Priya Shah, Threat Intel, Singapore
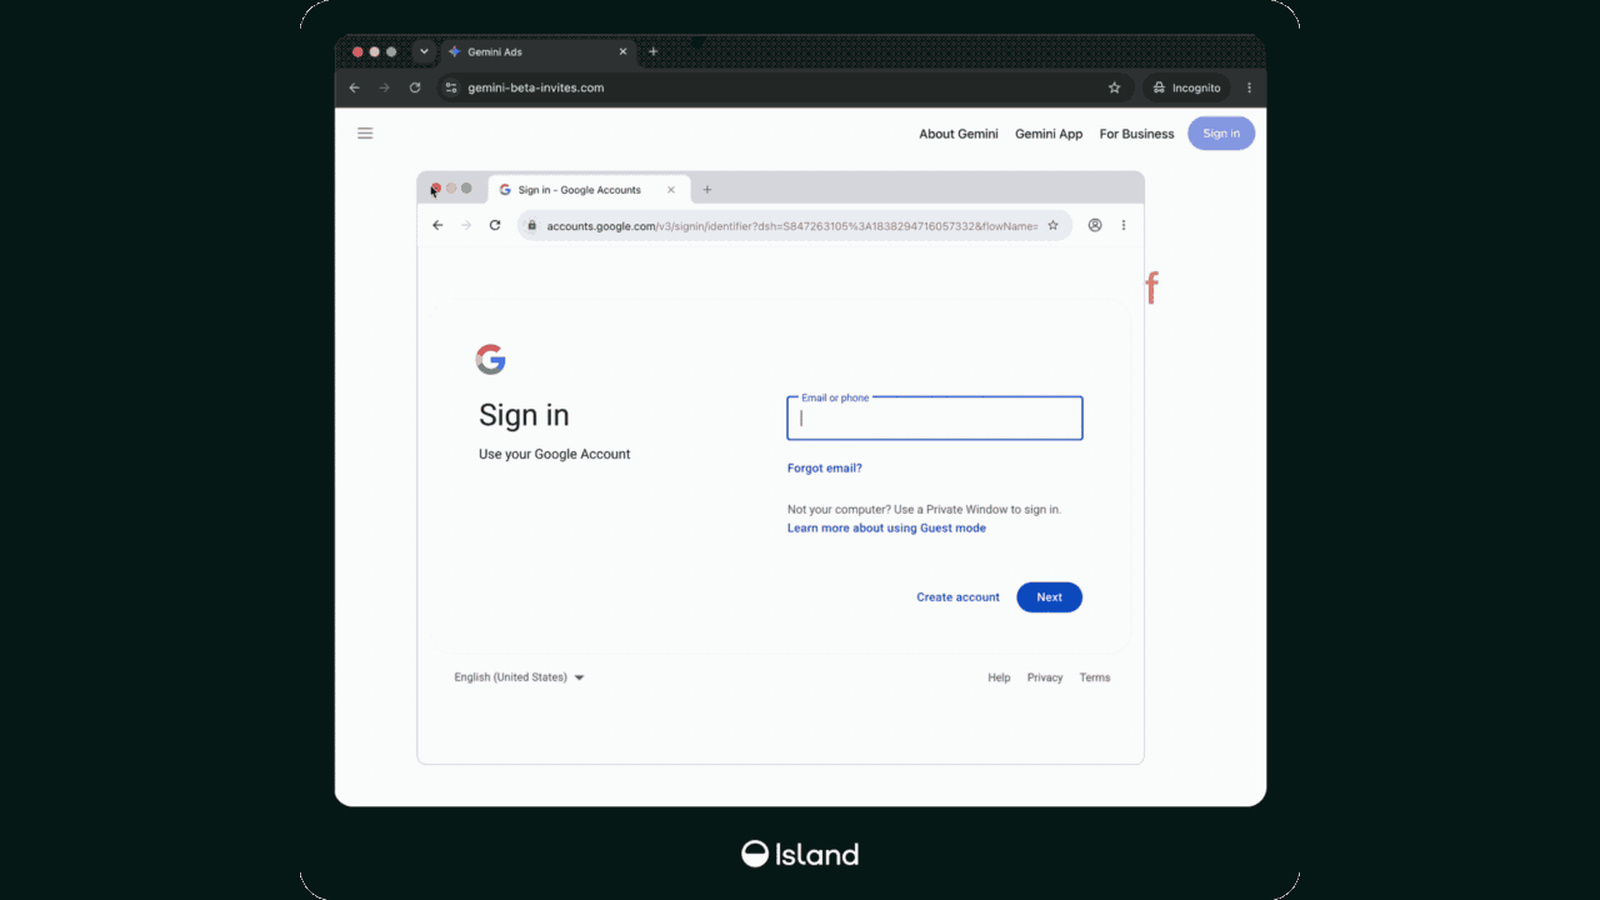
Read the storyScreenshot: Island, clicking Connect on a spoofed Gemini Ads page opens a fake Google sign-in window drawn inside the page while the real address bar still shows gemini-beta-invites.com, Oct 6, 2026 (fair use).
Island researchers said on October 6 that a human-operated phishing platform posing as AI advertising products for Gemini, ChatGPT, Claude, Perplexity and a fake Muse Ads draws a counterfeit Google sign-in window inside the page, then lets a live operator choose which MFA prompt the victim sees next.
Priya Shah, Threat Intel, Singapore
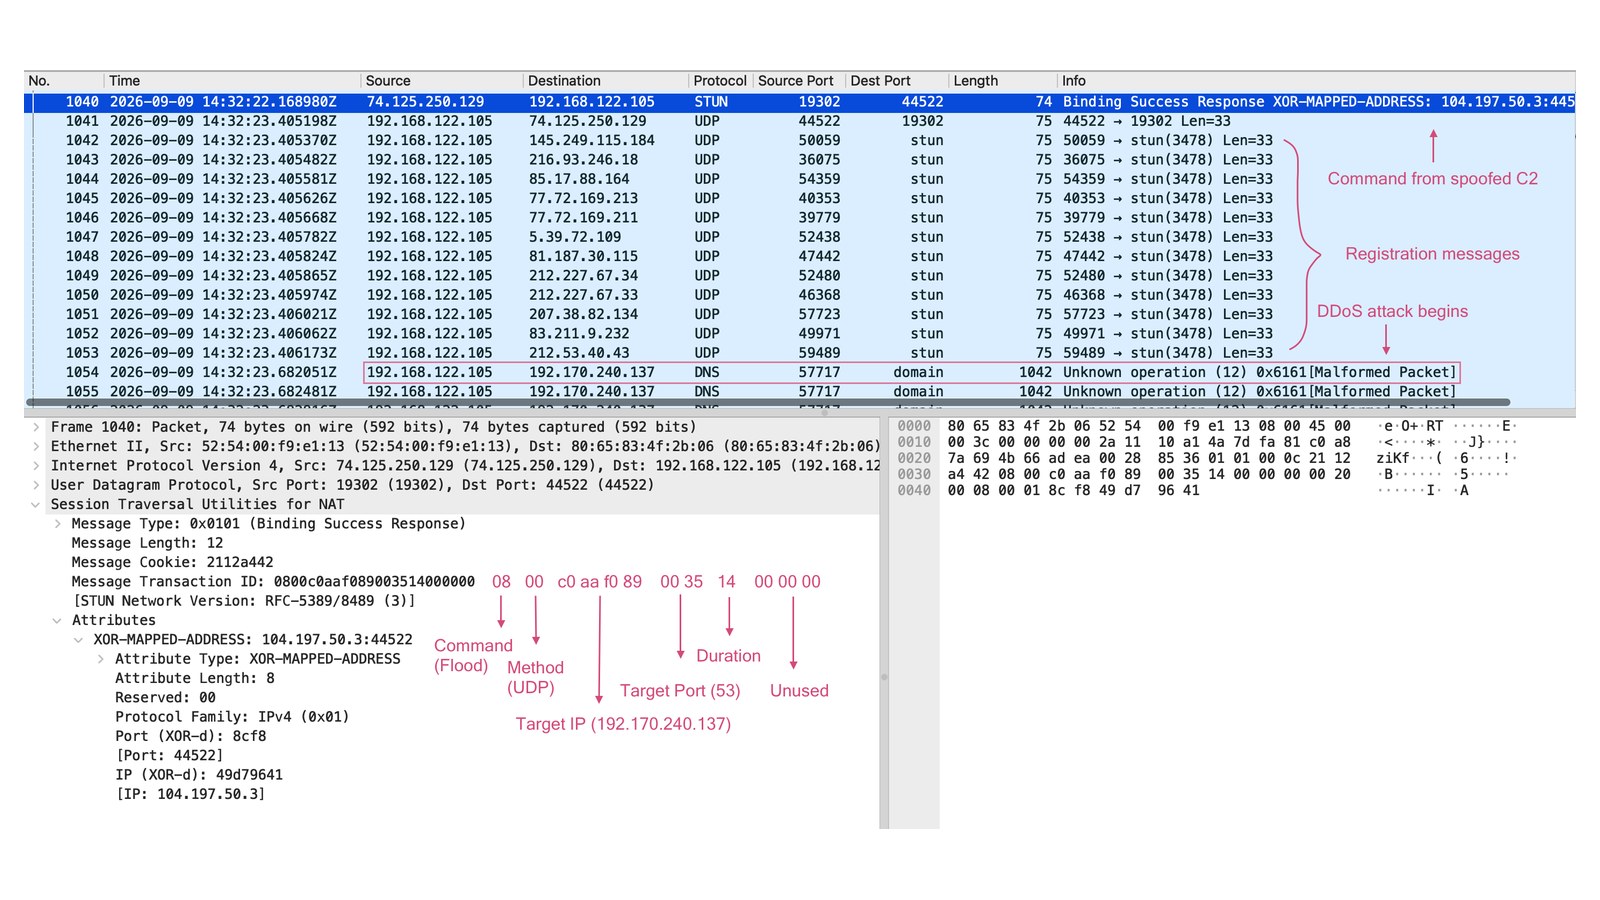
Read the storyScreenshot: Nozomi Networks Labs packet capture of a spoofed STUN reply carrying a flood command in its transaction ID, Oct 1, 2026 (fair use).
FortiGuard Labs said on October 5 that ClingSTUN, a Linux backdoor spread through 24 known flaws in routers, cameras and other edge devices, uses legitimate public STUN servers so its traffic blends with VoIP and WebRTC. Nozomi Networks, tracking the same malware as Cling, found operator commands hidden in STUN transaction IDs.
Priya Shah, Threat Intel, Singapore
Read the storyPhoto/figure: Rapid7 Labs research art, Sleeper Cells in the Telecom Backbone hero (fair use).
Rapid7 Intelligence published its first research drop on October 2, 2026, documenting Linux implants that impersonate South Korean SpamSniper and Taiwanese ShareTech mail-security appliances, with BPFDoor, Rekoobe, and a modular tool Rapid7 tracks as AVERAT blending command-and-control into SMTP traffic on the network edge.
Priya Shah, Threat Intel, Singapore
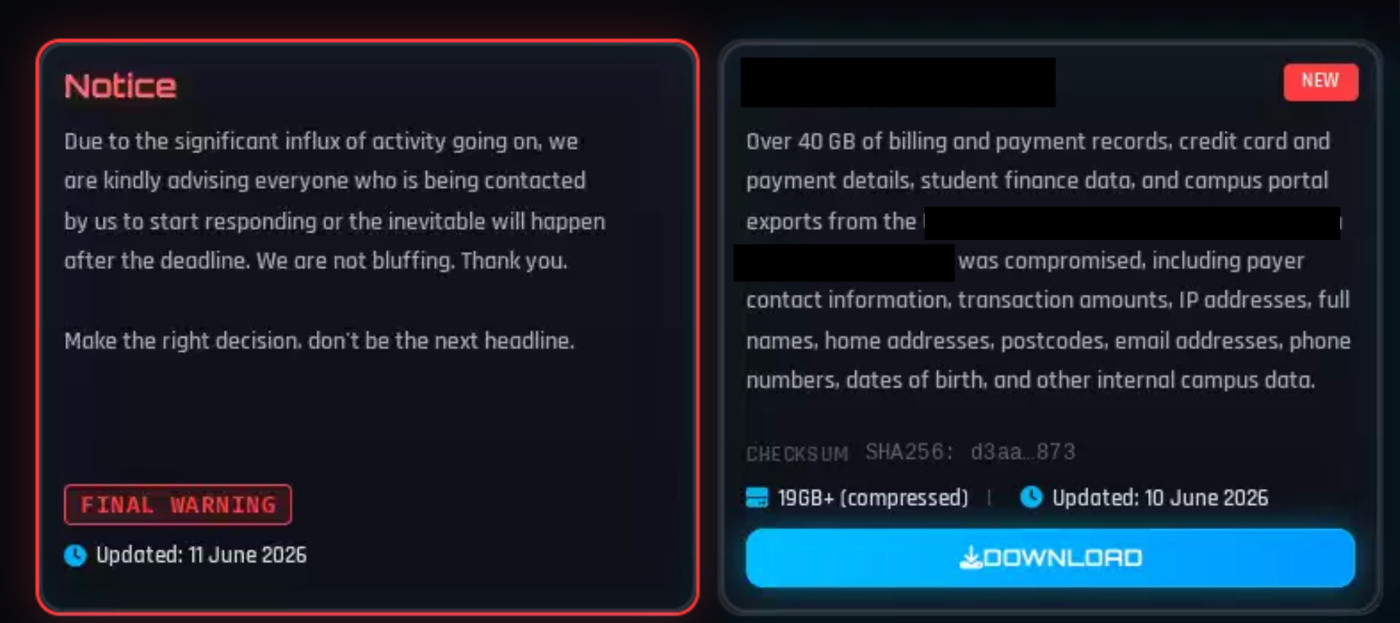
Read the storyLeak-site notice and data listing. Identifiers redacted.
Mandiant and Google Threat Intelligence Group say UNC6240, tracked as ShinyHunters, is again exploiting PeopleSoft CVE-2026-35273 by requesting a URL-encoded PSEMHUB path that literal WAF rules miss.
SINGAPORE - Arista Advisory 0183, published September 22, 2026 and revised to 1.1 on September 23, 2026, covers CVE-2026-93952 in the on-premises VeloCloud Orchestrator. The flaw was discovered externally and is actively exploited.
SAN JOSE - Cisco Talos researchers have documented CLOSEDQUORUM, which they describe as the first publicly reported Windows implant in their knowledge that uses a panel of commercial large language models as tactical command and control after deployment. The finding appears in a Talos blog by Ryan Fetterman dated Tuesday, September 22, 2026, and was uncovered with CAIRN, Talos' new open-source toolkit for tracking AI-integrated malware. Talos has not confirmed in-the-wild deployment.