Response, New York. Noah Park: Check Point Patches Actively Exploited Management Server Path Traversal. Detection, Dallas. Ava Okello: Report Finds Nearly Half of Deployed Detections Need Attention Before SOCs Can Trust Them.
RESPONSEHuntress Reconstructs Akira Ransomware Attack From Registry Artifacts After Post-Compromise EDR InstallNEW YORKNoah ParkDETECTIONCrowdStrike Shows Attackers Bypass LLM Safety Classifiers by Splitting Harmful Goals Into Benign SubtasksLONDONAva OkelloTOOLSUnit 42 Tracks ChainDrop and PolinRider Stealing Cloud Build Credentials Through Blockchain C2 Dead DropsAUSTINJames WhitfordTHREAT INTELCisco Talos Tracks UAT-11985 Phishing Taiwan Researchers With AI-Assisted Invites and Real-Time Google Login RelaysSINGAPOREPriya ShahRESPONSEHuntress Sees Active Exploitation of AhsayCBS Backup Flaws Dropping Webshells and XMRig Across Five OrganizationsNEW YORKNoah ParkDETECTIONMalware Now Embeds Instructions Meant to Steer AI Analysis Tools, Cisco Talos Finds Across 84 SamplesLONDONAva OkelloTHREAT INTELRussia-Aligned Spies Retool MATCHBOIL Malware and Widen Attacks to Ukrainian Transport, Manufacturing and Energy FirmsSINGAPOREPriya ShahRESPONSEFBI and Secret Service Warn FortiBleed Hackers Are Locking Some Fortinet Customers Out of Their Own FirewallsNEW YORKNoah ParkDETECTIONAttackers Are Testing Stolen AWS Keys for Amazon Bedrock Access, Leaving a Pattern Defenders Can SpotLONDONAva OkelloRESPONSEPoisoned Tensorlake npm Release Hid a Worm That Deletes Home Directories if Victims Revoke the Stolen TokenNEW YORKNoah ParkTHREAT INTELFBI Seizes Integrity Tech Hacking Tools as Allies Detail How China-Linked Hackers Steal Government EmailSINGAPOREPriya ShahDETECTIONMalware That Reads Its Orders From a Poem on GitHub Has Hit More Than 3,400 Exposed AI and Developer ServersLONDONAva OkelloTHREAT INTELIran-Linked Hackers Posing as Dubai Airports Recruiters Hide Malware in a Visual Studio Coding TestSINGAPOREPriya ShahTHREAT INTELFake ChatGPT and Gemini Ad Portals Use Browser-in-the-Browser Pop-Ups to Steal Logins and MFA CodesSINGAPOREPriya ShahDETECTIONMicrosoft Warns ClickFix Lures Now Hide Their Payload in the Browser CacheLONDONAva OkelloTHREAT INTELClingSTUN Backdoor Turns Unpatched IoT Devices Into Proxies Hidden in Public STUN TrafficSINGAPOREPriya ShahDETECTIONThales SConnect Flaw Opened Drive-By Code Execution on PCs Used for SWIFT 3SKey Sign-InLONDONAva OkelloRESPONSECitrix Patches NetScaler SAML Zero-Day CVE-2026-88779 After Attacks Reboot Freshly Patched AppliancesNEW YORKNoah ParkTHREAT INTELRapid7 Tracks BPFDoor and AVERAT Implants Mimicking Asian Mail GatewaysSINGAPOREPriya ShahRESPONSEMicrosoft Tracks Unauthenticated Zimbra SNMP Command Injection Exploited as CVE-2026-73570NEW YORKNoah ParkOPINIONSOC Autonomy Without Governance Recreates the Same Failure Modes AI Was Meant to FixLONDONElena VosTHREAT INTELMandiant Warns ShinyHunters Bypass WAFs to Resume PeopleSoft Mass ExploitationSINGAPOREPriya ShahDETECTIONMicrosoft Tracks EvilTokens Phishing Kit Behind Device Code Token TheftLONDONAva OkelloRESPONSECitrix Confirms Two NetScaler RCE Zero-Days Exploited in the WildNEW YORKNoah ParkDETECTIONHuntress Finds Threat Actor Compiling Silent XMR Miner Directly on EndpointLONDONAva OkelloRESPONSECISA Puts MikroTik RouterOS SSH Workflow Flaw CVE-2026-67279 on KEVWASHINGTONNoah ParkRESPONSECheck Point Patches Actively Exploited Management Server Path TraversalNEW YORKNoah ParkDETECTIONReport Finds Nearly Half of Deployed Detections Need Attention Before SOCs Can Trust ThemDALLASAva OkelloRESPONSEHuntress Reconstructs Akira Ransomware Attack From Registry Artifacts After Post-Compromise EDR InstallNEW YORKNoah ParkDETECTIONCrowdStrike Shows Attackers Bypass LLM Safety Classifiers by Splitting Harmful Goals Into Benign SubtasksLONDONAva OkelloTOOLSUnit 42 Tracks ChainDrop and PolinRider Stealing Cloud Build Credentials Through Blockchain C2 Dead DropsAUSTINJames WhitfordTHREAT INTELCisco Talos Tracks UAT-11985 Phishing Taiwan Researchers With AI-Assisted Invites and Real-Time Google Login RelaysSINGAPOREPriya ShahRESPONSEHuntress Sees Active Exploitation of AhsayCBS Backup Flaws Dropping Webshells and XMRig Across Five OrganizationsNEW YORKNoah ParkDETECTIONMalware Now Embeds Instructions Meant to Steer AI Analysis Tools, Cisco Talos Finds Across 84 SamplesLONDONAva OkelloTHREAT INTELRussia-Aligned Spies Retool MATCHBOIL Malware and Widen Attacks to Ukrainian Transport, Manufacturing and Energy FirmsSINGAPOREPriya ShahRESPONSEFBI and Secret Service Warn FortiBleed Hackers Are Locking Some Fortinet Customers Out of Their Own FirewallsNEW YORKNoah ParkDETECTIONAttackers Are Testing Stolen AWS Keys for Amazon Bedrock Access, Leaving a Pattern Defenders Can SpotLONDONAva OkelloRESPONSEPoisoned Tensorlake npm Release Hid a Worm That Deletes Home Directories if Victims Revoke the Stolen TokenNEW YORKNoah ParkTHREAT INTELFBI Seizes Integrity Tech Hacking Tools as Allies Detail How China-Linked Hackers Steal Government EmailSINGAPOREPriya ShahDETECTIONMalware That Reads Its Orders From a Poem on GitHub Has Hit More Than 3,400 Exposed AI and Developer ServersLONDONAva OkelloTHREAT INTELIran-Linked Hackers Posing as Dubai Airports Recruiters Hide Malware in a Visual Studio Coding TestSINGAPOREPriya ShahTHREAT INTELFake ChatGPT and Gemini Ad Portals Use Browser-in-the-Browser Pop-Ups to Steal Logins and MFA CodesSINGAPOREPriya ShahDETECTIONMicrosoft Warns ClickFix Lures Now Hide Their Payload in the Browser CacheLONDONAva OkelloTHREAT INTELClingSTUN Backdoor Turns Unpatched IoT Devices Into Proxies Hidden in Public STUN TrafficSINGAPOREPriya ShahDETECTIONThales SConnect Flaw Opened Drive-By Code Execution on PCs Used for SWIFT 3SKey Sign-InLONDONAva OkelloRESPONSECitrix Patches NetScaler SAML Zero-Day CVE-2026-88779 After Attacks Reboot Freshly Patched AppliancesNEW YORKNoah ParkTHREAT INTELRapid7 Tracks BPFDoor and AVERAT Implants Mimicking Asian Mail GatewaysSINGAPOREPriya ShahRESPONSEMicrosoft Tracks Unauthenticated Zimbra SNMP Command Injection Exploited as CVE-2026-73570NEW YORKNoah ParkOPINIONSOC Autonomy Without Governance Recreates the Same Failure Modes AI Was Meant to FixLONDONElena VosTHREAT INTELMandiant Warns ShinyHunters Bypass WAFs to Resume PeopleSoft Mass ExploitationSINGAPOREPriya ShahDETECTIONMicrosoft Tracks EvilTokens Phishing Kit Behind Device Code Token TheftLONDONAva OkelloRESPONSECitrix Confirms Two NetScaler RCE Zero-Days Exploited in the WildNEW YORKNoah ParkDETECTIONHuntress Finds Threat Actor Compiling Silent XMR Miner Directly on EndpointLONDONAva OkelloRESPONSECISA Puts MikroTik RouterOS SSH Workflow Flaw CVE-2026-67279 on KEVWASHINGTONNoah ParkRESPONSECheck Point Patches Actively Exploited Management Server Path TraversalNEW YORKNoah ParkDETECTIONReport Finds Nearly Half of Deployed Detections Need Attention Before SOCs Can Trust ThemDALLASAva Okello
Huntress shows how Shellbags, Akira logs, and PowerShell shadow-copy toolmarks reconstructed an Akira intrusion after a post-compromise agent install left only a thin EDR slice of GOST tunneling and related activity.
Noah Park, Response, New York
Read the storyGraphic: Huntress, Rapid Response header art for the Oct 8, 2026 AhsayCBS active-exploit post (fair use).
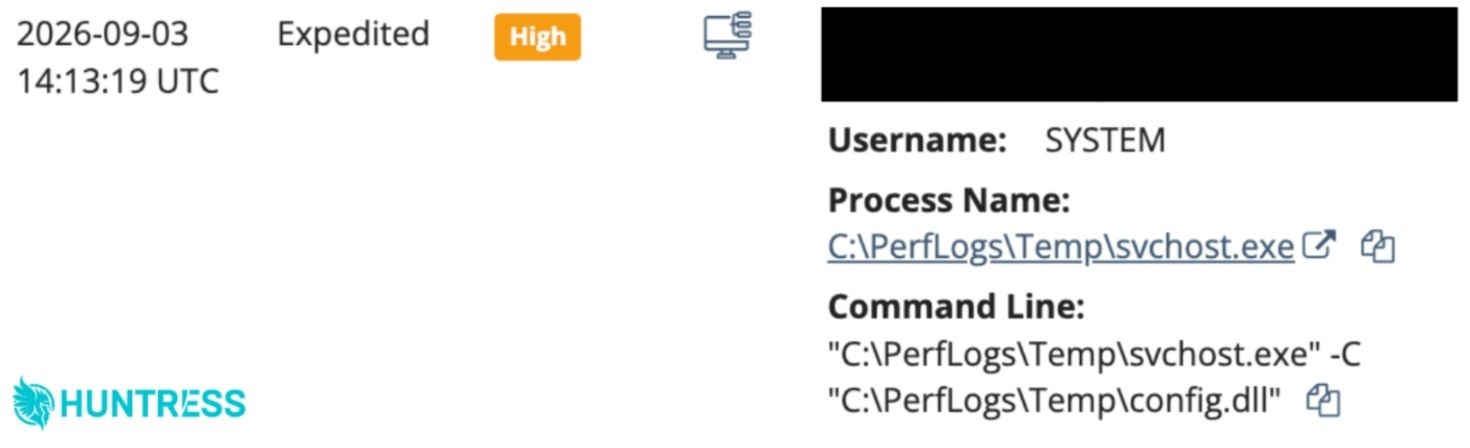
Huntress says attackers began chaining two AhsayCBS flaws on Oct. 7 to gain SYSTEM-level remote code execution, then planted JSP webshells, an XMRig miner disguised as Microsoft Edge, and an AI-assisted PowerShell script that hides mining when Task Manager is open. Four Sigma rules and IOCs are published for defenders.
Noah Park, Response, New York
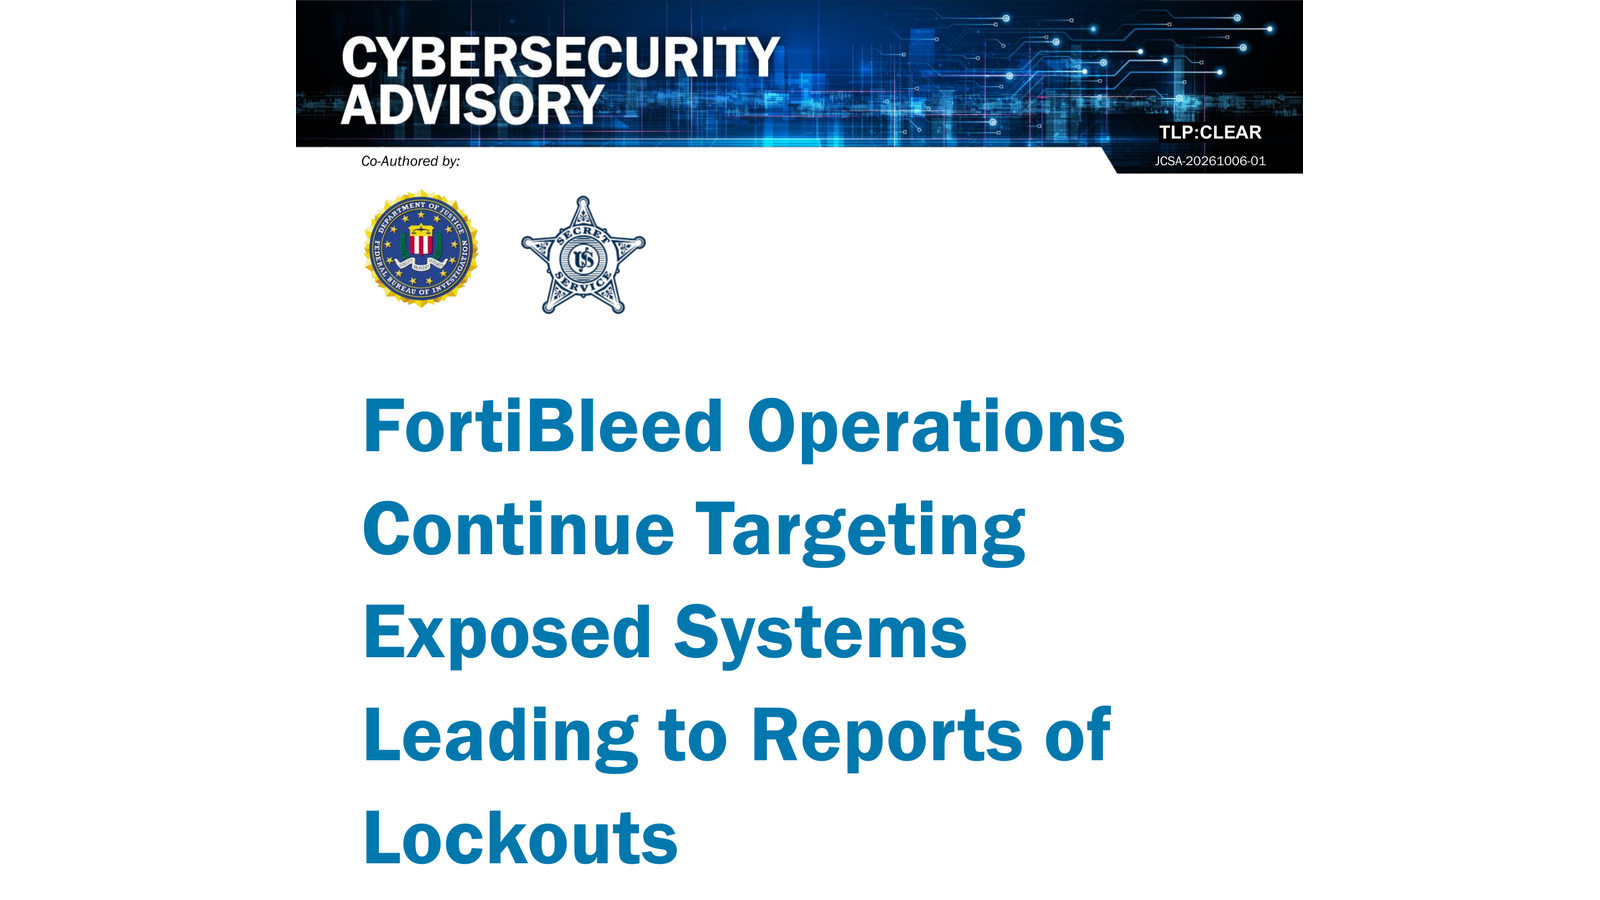
Read the storyDocument: FBI and U.S. Secret Service, cover of joint cybersecurity advisory JCSA-20261006-01, FortiBleed Operations Continue Targeting Exposed Systems Leading to Reports of Lockouts, Oct 6, 2026 (fair use).
A joint FBI and Secret Service advisory says the credential theft campaign against internet-facing FortiGate firewalls is still scanning with stolen passwords, sometimes deletes or changes administrators' accounts so owners cannot log in, and has fed access to the INC/Lynx and Payload ransomware operations.
Noah Park, Response, New York
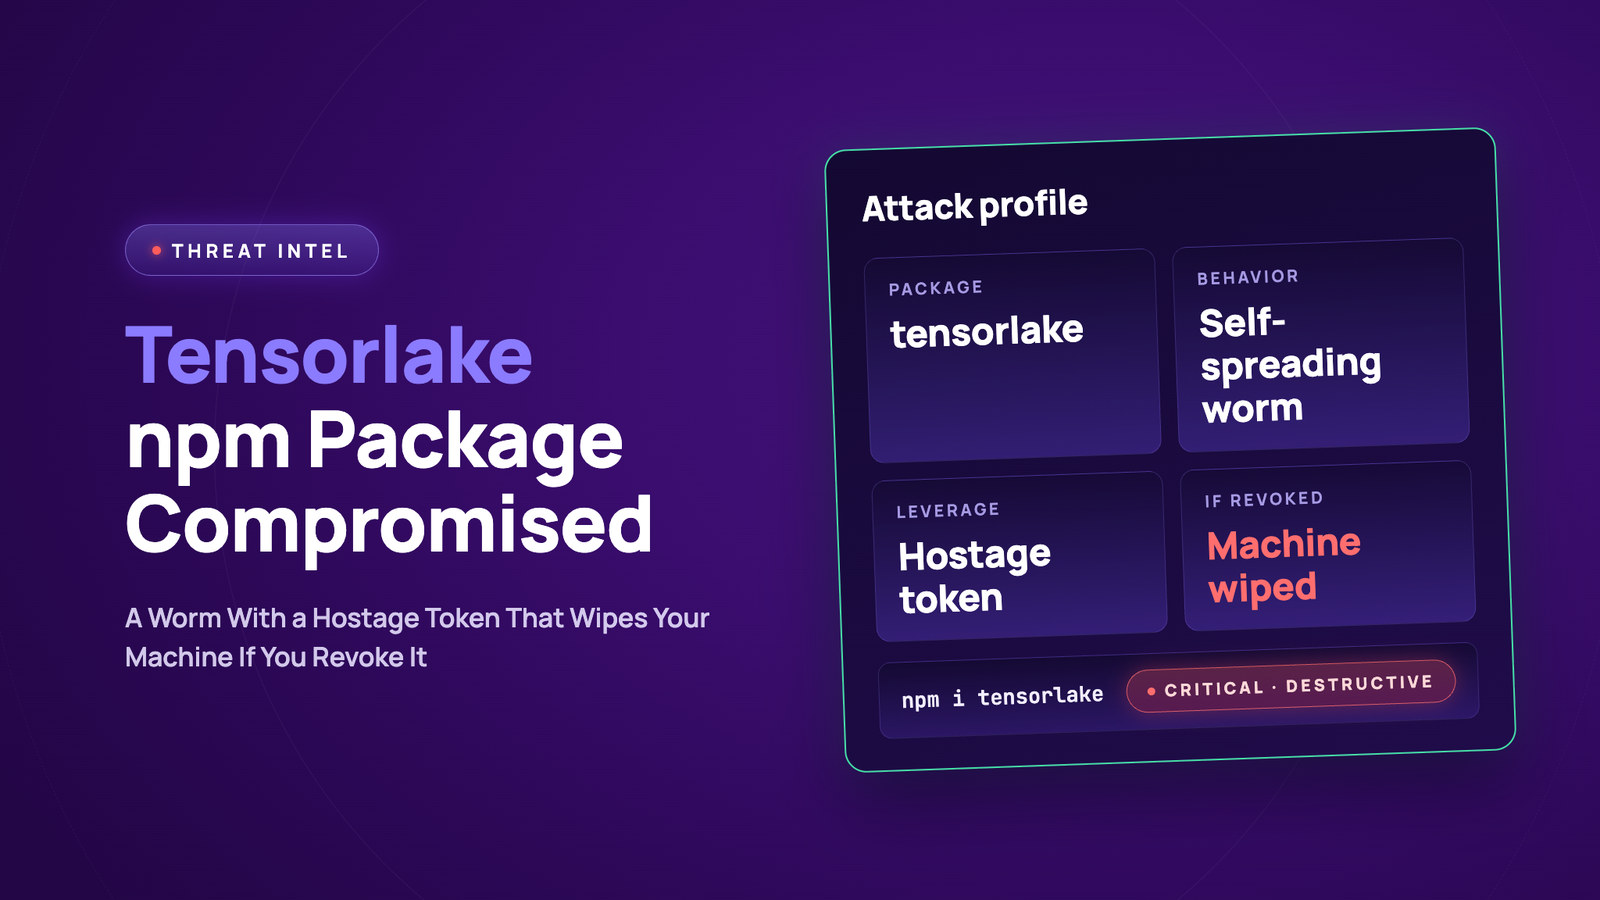
Read the storyGraphic: StepSecurity, summary of the tensorlake npm compromise, a self-spreading worm that holds a stolen GitHub token hostage and wipes the machine if the token is revoked, Oct 8, 2026 (fair use).
A malicious tensorlake 0.5.144, pushed to the AI sandbox company's own GitHub repository and published with valid npm provenance on October 8, steals cloud, GitHub and npm secrets, spreads through victims' packages and installs a monitor that deletes the home directory if the stolen GitHub token is revoked, so responders must remove it before rotating credentials.
Noah Park, Response, New York
Read the storyImage: The Hacker News, NetScaler SAML service-unavailable illustration (fair use).
Citrix shipped its second emergency NetScaler update in a week after attackers crashed SAML-enabled gateways that had already been patched for the PitScaler flaws, and incident responders say the forced reboots are being used to fire earlier log-injection payloads on appliances that missed the first fix.
Noah Park, Response, New York
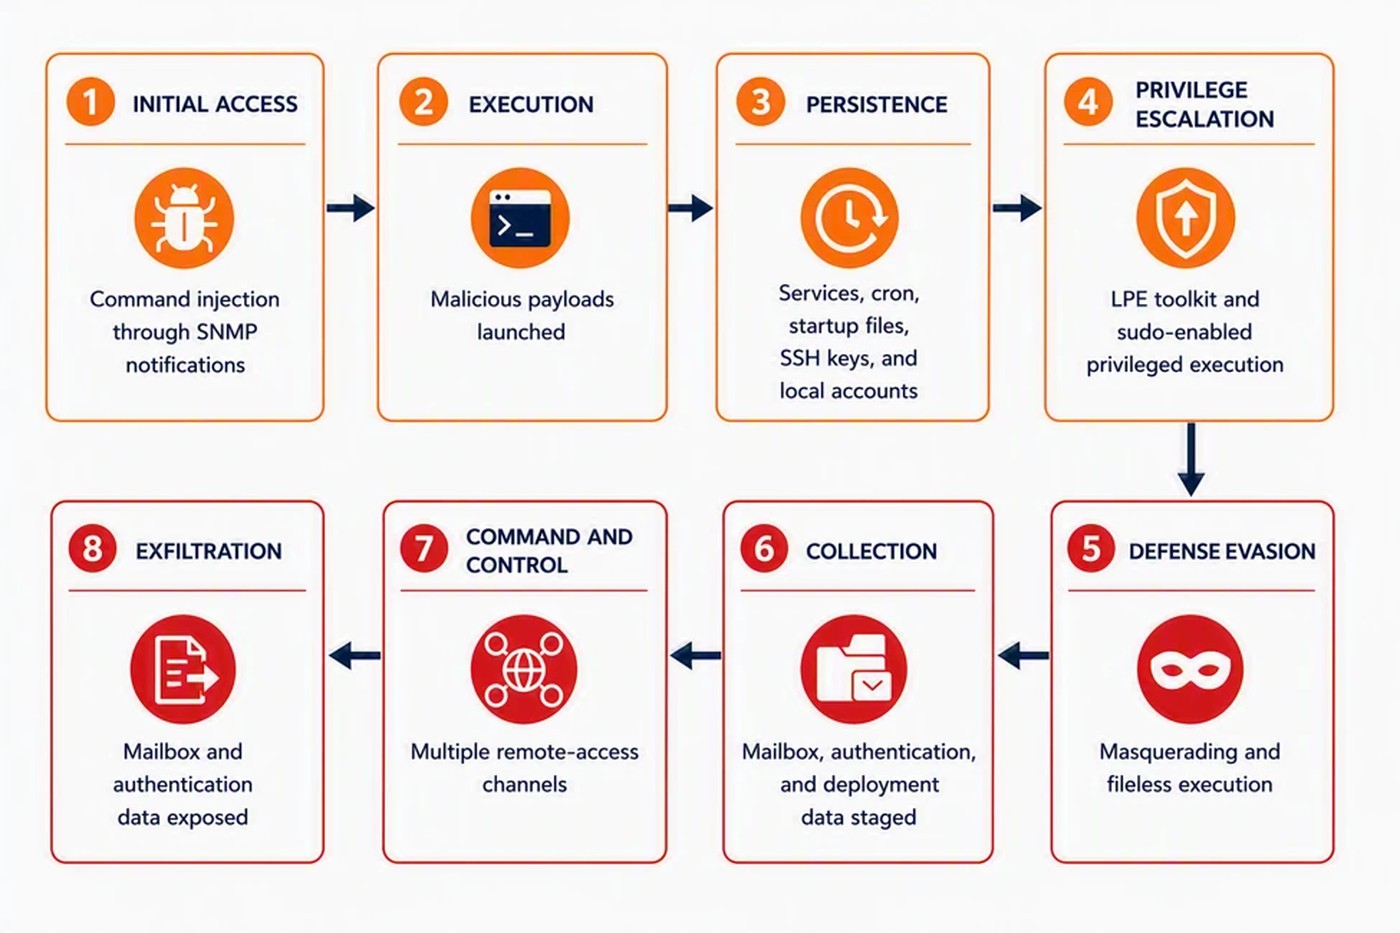
Read the storyPhoto/figure: Microsoft Security Research / Microsoft Security Blog, Sep 30, 2026. Figure 1. CVE-2026-73570 attack chain (fair use).
Microsoft Security Research published findings on September 30, 2026, tracking unauthenticated OS command injection in the Zimbra Collaboration Suite SNMP notification path as CVE-2026-73570, with post-exploitation webshells, privilege escalation, credential theft, and mailbox staging observed on internet-facing mail servers.
Citrix says exploits of CVE-2026-88771 and CVE-2026-88772 have been observed on unmitigated NetScaler ADC and Gateway deployments, and CISA added both flaws to the KEV catalog on September 27, 2026.
Noah Park, Response, New York
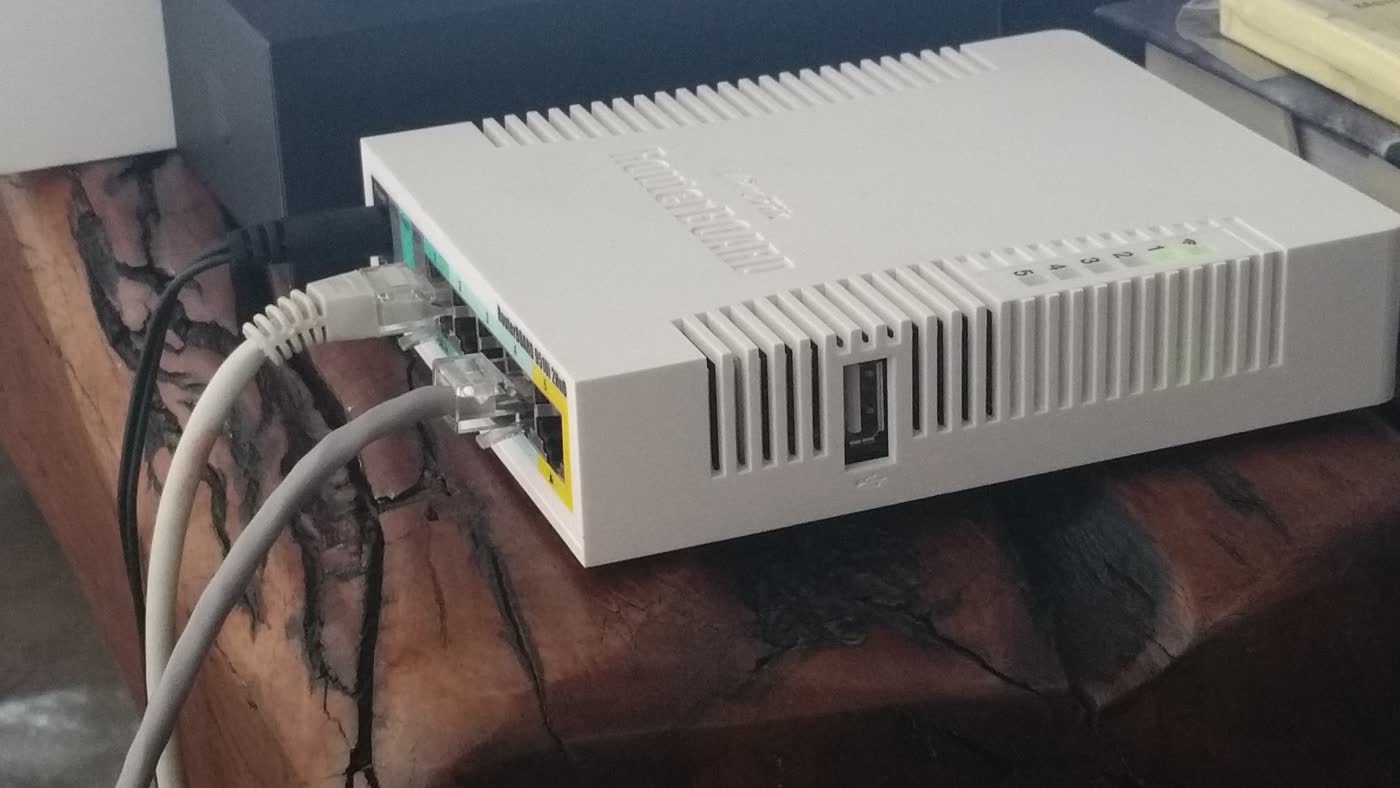
Read the storyPhoto: Deavmi. MikroTik RB951Ui-2HnD. CC BY-SA 3.0 Wikimedia.
Federal agencies have until September 28 to remediate internet-exposed RouterOS devices after CISA confirmed active exploitation of the SSH state-machine bug used in the MikroTrick takeover chain.
NEW YORK - For security operations teams, this is a VPN and remote-access control-plane incident, not only a gateway patch ticket, and it is distinct from the management-plane path traversal CVE-2026-93616 that Check Point disclosed in the same advisory wave. Priority work is inventory of gateways and Spark hosts still on vulnerable trains with certificate-based Site-to-Site or Remote Access VPN; installation of LivePatch Take 26 or the matching Jumbo or Spark build; and log review for anomalous certificate-based Mobile Access logins since September 12, without limiting the hunt to the three published subjects. Check Point also advises looking for second-stage internal port and service scanning from suspicious Mobile Access users. If patching is delayed, the vendor recommends disabling VPN implied rules and restricting Site-to-Site UDP/500 and UDP/4500 to peer IP addresses (and for Remote Access, the required UDP and TCP services), noting that those temporary mitigations do not apply to locally managed Spark firewalls. Confirmed or suspected compromise should trigger forensic triage before operators treat residual risk as closed on patch status alone.
NEW YORK - F5 Networks has confirmed a critical heap-based buffer overflow in BIG-IP Access Policy Manager is under active exploitation, and CISA added it to the Known Exploited Vulnerabilities catalog.
WASHINGTON - The Cybersecurity and Infrastructure Security Agency has updated its Known Exploited Vulnerabilities catalog so that CVE-2026-63077, a critical JetBrains TeamCity On-Premises flaw, is now marked with known ransomware campaign use. Trade press reported the KEV change on Wednesday, September 23, 2026. CISA first added the vulnerability to the catalog on August 5, 2026, after evidence of active exploitation. The live KEV feed lists knownRansomwareCampaignUse as Known for this CVE.
Patchstack and other defenders report pearcmd-based file writes against unpatched WordPress after CVE-2026-87902 disclosure, turning a template-resolution path traversal into a SOC containment problem.
CISA added a critical WSO2 API Manager JWT authentication bypass to KEV on September 24, giving federal agencies until September 27 and pushing SOCs to treat exposed gateways as an auth-plane incident.
CISA put an unauthenticated Adobe Commerce and Magento incorrect-authorization flaw on KEV on September 24, giving agencies until September 27 and pushing SOCs to treat exposed storefronts as session-hijack cases.
WASHINGTON - When CISA adds a vulnerability to the Known Exploited Vulnerabilities catalog and flags forensic triage, the agency's Binding Operational Directive 26-04 implementation guidance tells responders to collect evidence before they patch. Patching first can destroy the artifacts that show whether an adversary already used the hole.