Microsoft folds SIEM and threat protection into Defender as ISOC enters preview
Ava Okello, DetectionLondon2 min read
REDMOND - Microsoft on September 23, 2026, announced Integrated Security Operations Center, or ISOC, in Microsoft Defender, a preview foundation that puts security information and event management and native threat protection on one shared platform so analysts and agents can investigate and act without stitching separate stacks.
In a Microsoft Security Blog post the same day, Rob Lefferts, Corporate Vice President for Microsoft Threat Protection, argued that agent-driven attacks have changed the economics of defense. Attackers can automate execution at scale, he wrote, while defenders still lose time at every handoff, integration, and boundary between protection and operations. ISOC is Microsoft's answer: security operations and native protection functioning as one system inside Defender, giving people and agents a shared foundation to see, understand, and act across the environment.
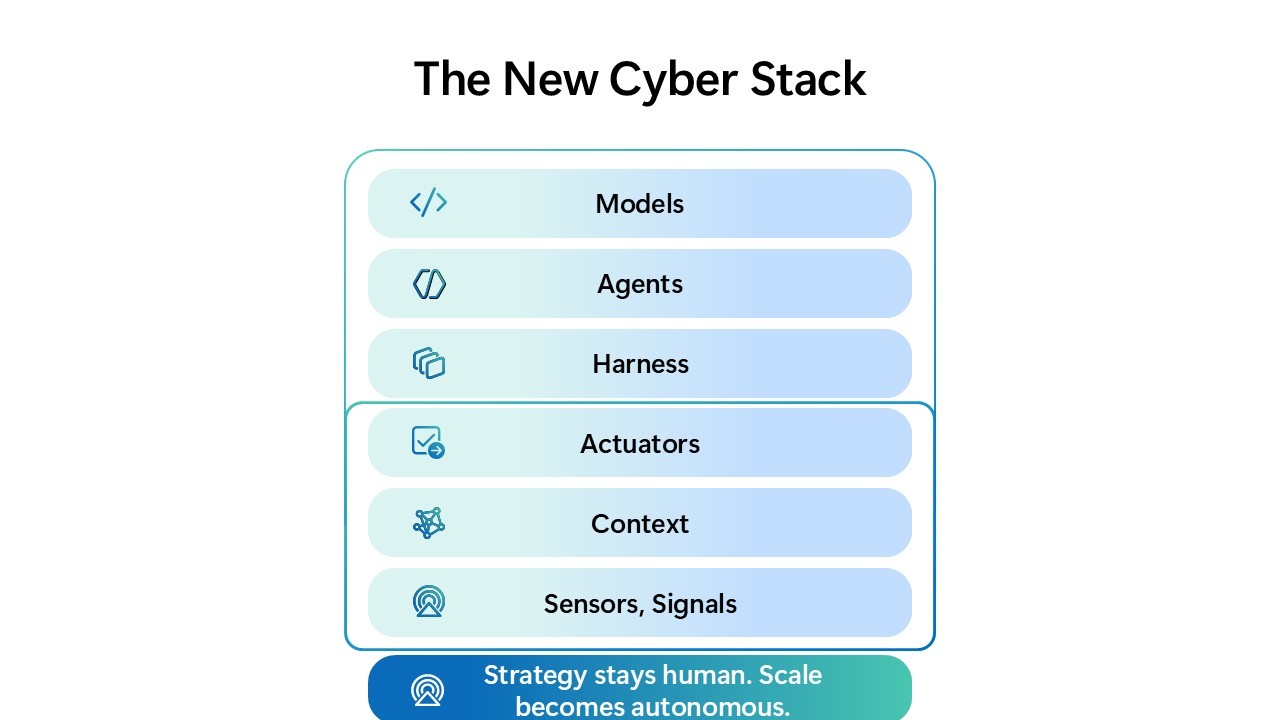
ISOC sits on the operations layer of the agentic stack Microsoft described in July 2026 alongside Project Perception. That earlier push focused on models, a harness, and specialized agents meant to help defenders perceive, reason, and act at machine speed. Lefferts said intelligence and orchestration alone are not enough. Agents need signals and sensors for visibility, context that turns signals into understanding, and actuators that translate decisions into protection. With ISOC, Microsoft said those layers are meant to work in unison so agents move beyond isolated tasks and help operate an agentic SOC. The company is explicit that agents supply continuous speed and scale while people set priorities, apply judgment, and define outcomes.
Microsoft pointed to Attack Disruption in Defender as an example of the integrated protection loop it wants to make native. Rich telemetry and controls, it said, let the system detect, predict, and adapt while an attack is still unfolding, disrupt threats in progress, and use exposure insights and threat intelligence to strengthen protection in near real time. Under ISOC, investigate, hunt, automate, incident-management, and response capabilities are positioned as available by default in one place rather than assembled and maintained by each customer across tool boundaries.
ISOC remains in preview. It is not a standalone product and is not a vendor-neutral SIEM.
Microsoft Learn says the preview applies to Microsoft Defender XDR and to Microsoft Sentinel in the Defender portal. Eligible customers are those with Microsoft Defender Suite or Microsoft 365 E5/E7 who do not have an active Microsoft Sentinel workspace. During this phase they receive 30 days of included retention for Defender data. Learn says not to disconnect a production Sentinel workspace only to qualify. Microsoft has also described November 15 2026 as the date when included retention is due to lengthen and when existing Sentinel customers who meet the license criteria can choose to move to ISOC.
Sources:
Ava Okello covers detection engineering and alert operations for SOCtember from London.