SOC Autonomy Without Governance Recreates the Same Failure Modes AI Was Meant to Fix
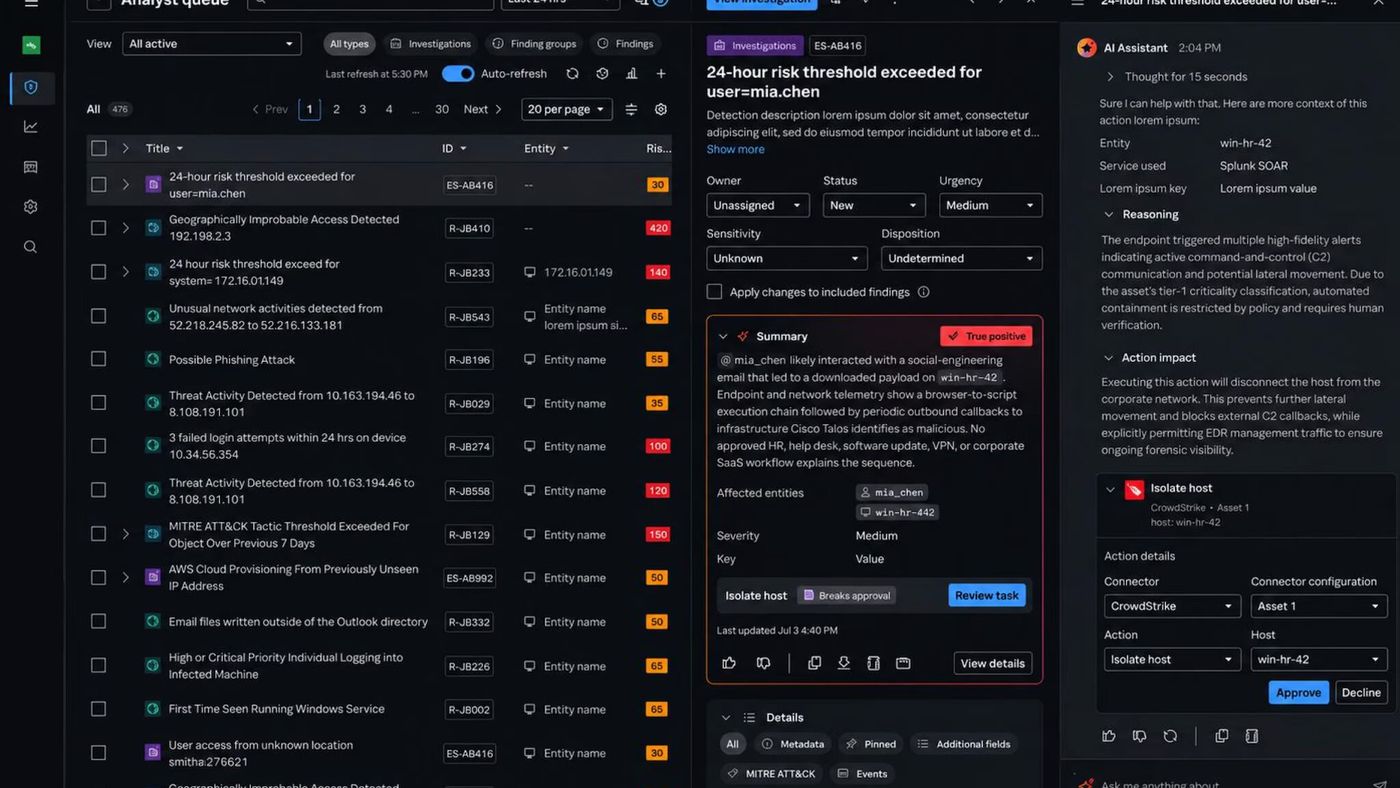
Splunk Enterprise Security 8.7 frames the Agentic SOC as a move from AI-assisted investigation to governed autonomous response, where permitted actions, approval gates, evidence, policy, and auditability matter more than buying a stronger model.
Elena Vos, OpinionLondon5 min read
LONDON - Security operations leaders who treat agentic response as a model-capability purchase will recreate the same failure modes artificial intelligence was supposed to fix. The practical question is not whether an assistant can summarize an alert faster. It is whether the SOC can govern autonomous action with evidence, approvals, policy, auditability, and human accountability.
That is the frame Splunk put around Enterprise Security 8.7 in a September 30, 2026 product post by Abhik Mitra. The release, available since September 2, 2026, is positioned as a step from AI-assisted investigation toward governed autonomous response. The company's own language is useful for SOC operators precisely because it refuses to separate autonomy from controls.
The AI SOC Analyst update is the clearest example. Splunk says the analyst can use investigation and response-plan context to move from alert to action. It can execute permitted actions, complete response tasks, and recommend next steps when analyst approval is required. That last clause is not a marketing flourish. It is the operating boundary. Autonomy that can act only inside permission and that must surface a recommendation when policy demands a human is an operations-governance design, not a larger model.
The same pattern shows up in how automation and detection are supposed to scale. Connector Builder Agent is described as helping teams generate, test, and refine connectors so automation can extend across tools the SOC already uses. Detection Builder Agent includes improved reliability when creating and refining detections, with better SPL guidance and validation. Neither capability is valuable if teams treat generated connectors and detections as opaque wins. They matter when experts remain in control of what gets promoted into production.
Ecosystem context is framed the same way. Enterprise Security on MCP is presented as a way for AI applications to securely access ES investigation context, including alerts, entities, findings, and supporting data. View Change History adds complete change history available in SPL search. Trusted autonomy, in Splunk's own summary, depends on clarity: what happened, who changed it, what evidence supported it, and how the workflow moved forward.
Capabilities vary by edition and deployment model, and Splunk says customers should contact a representative to enable AI SOC Analyst features. Those caveats matter for procurement. They also underscore the Opinion point: buying a release that advertises agentic response does not install an operating model. Without explicit permission boundaries, approval paths, audit trails, and named human accountability, autonomous action becomes another channel for inconsistent response and unreviewable change.
This thesis is distinct from four other SOCtember Opinion lines. Alert fatigue as a detection-pipeline failure asks how noise is manufactured upstream. Detection engineering's false positive ownership gap asks why teams measure noise without prioritizing cuts. The Ponemon and Crogl investigation-coverage argument asks why most alerts never become cases even when AI promises speed. The SANS retention argument treats staffing and AI adoption as operations-design problems. The Splunk ES 8.7 framing sharpens a fifth claim: trusted autonomy is an operations-governance problem. Model capability without evidence, approvals, policy, auditability, and human accountability is an incomplete purchase.
Sources:
Elena Vos covers SOC strategy and detection operations for SOCtember from London.
Related stories
Opinion
Alert Fatigue Is a Detection Pipeline Failure, Not an Analyst Character Flaw
Response
Citrix Confirms Two NetScaler RCE Zero-Days Exploited in the Wild
Detection
Microsoft Tracks EvilTokens Phishing Kit Behind Device Code Token Theft
Threat Intel
Mandiant Warns ShinyHunters Bypass WAFs to Resume PeopleSoft Mass Exploitation
Tools