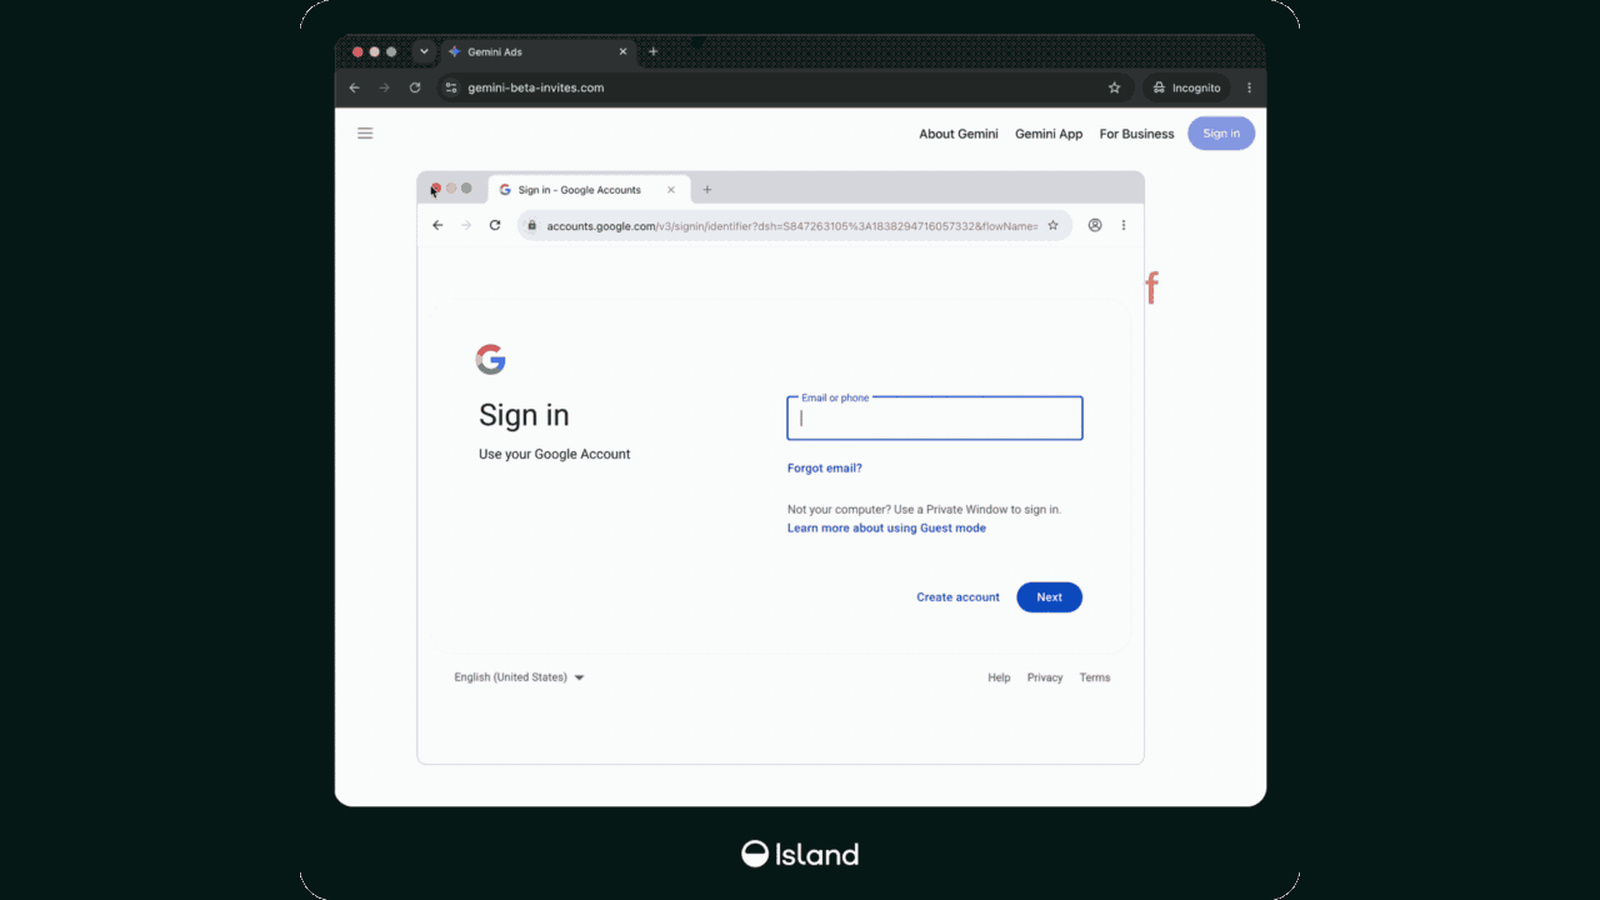
Fake ChatGPT and Gemini Ad Portals Use Browser-in-the-Browser Pop-Ups to Steal Logins and MFA Codes
Island researchers said on October 6 that a human-operated phishing platform posing as AI advertising products for Gemini, ChatGPT, Claude, Perplexity and a fake Muse Ads draws a counterfeit Google sign-in window inside the page, then lets a live operator choose which MFA prompt the victim sees next.
Priya Shah, Threat IntelSingapore5 min read
SINGAPORE - A phishing operation aimed at the people who run corporate advertising accounts is dressing itself up as a line of AI products, and the sign-in window it shows victims is not a window at all, researchers at the browser security company Island said on Tuesday. Pages posing as advertising tools for Gemini, ChatGPT, Claude, Perplexity and Manus, and most recently a fake "Muse Ads," all lead to the same button: Connect. "Clicking it opened a browser drawn inside the real browser," wrote Oleg Zaytsev and Ofek Ronen of Island. "The fake address bar displayed trusted origins such as accounts.google.com or an Okta tenant, while the real browser remained on the phishing domain." For security operations teams, the report matters less for the lure than for what sits behind it: a live operator who decides, step by step, which multifactor prompt the victim sees next.
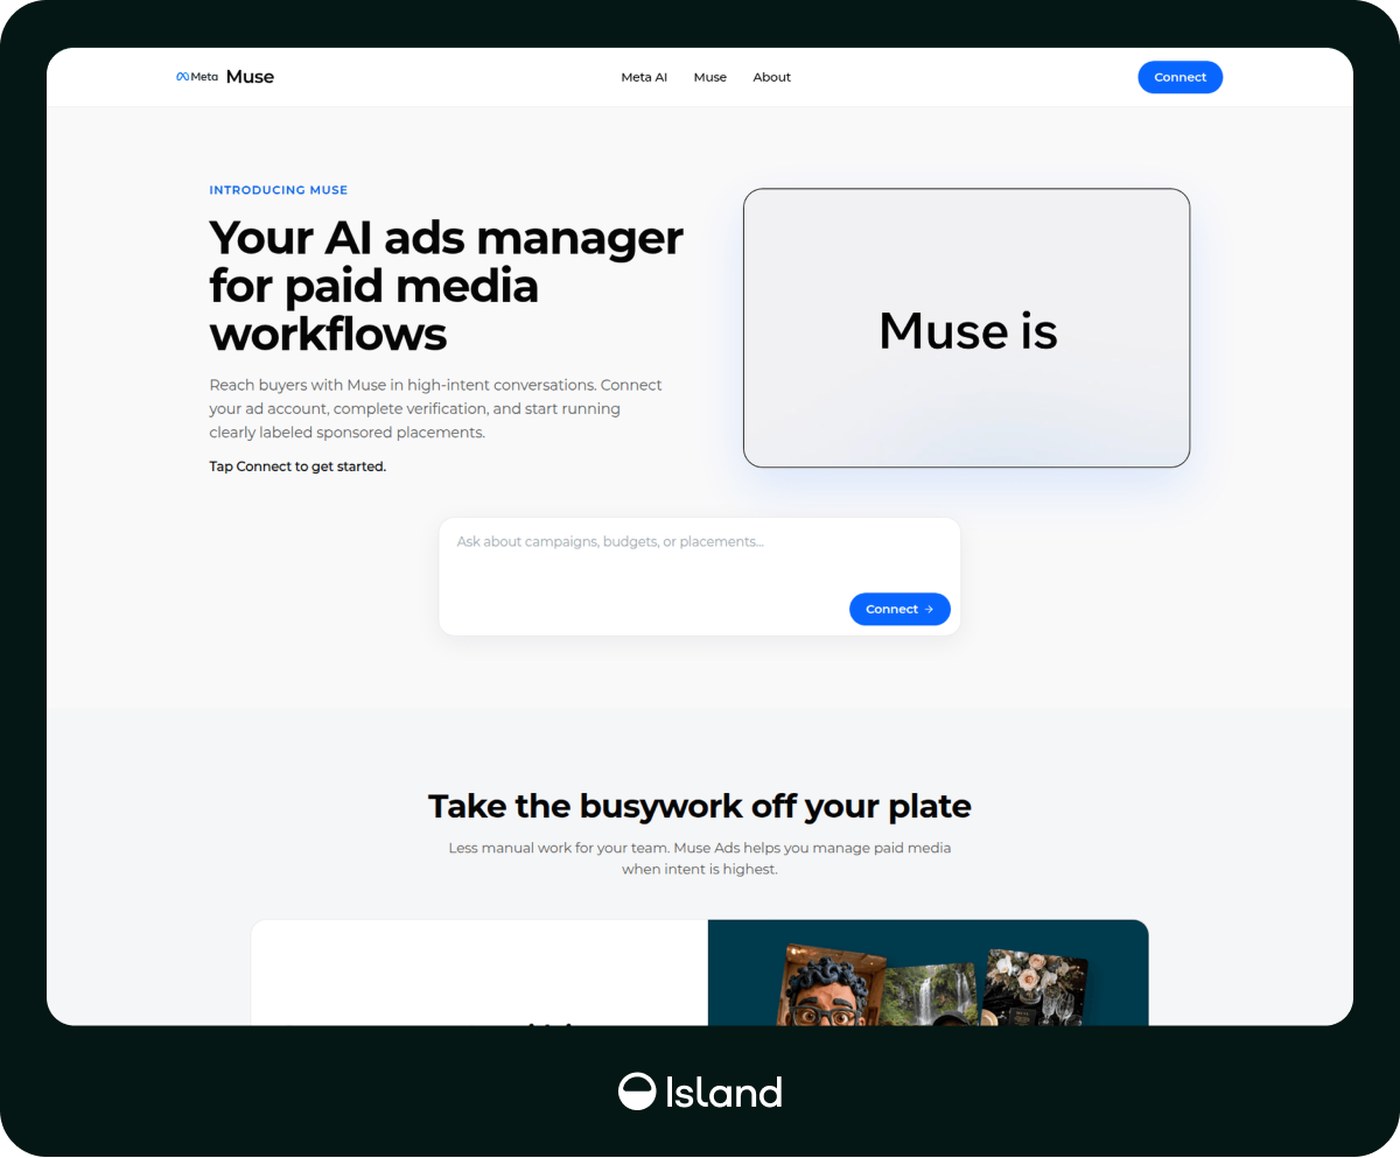
The newest lure moved with the news. Meta introduced Muse as a personal AI agent on September 8, according to Island, and by September 16 the domain museads.ai was presenting a product it called "Your AI ads manager for paid media workflows." Each brand gets its own pitch. The fake ChatGPT page promises a Monday Google Ads brief, the Gemini page promises support for manager accounts and linked clients, and the Perplexity page offers campaign planning and spend audits. The copy is written in advertiser shorthand like MCC and ROAS, Island said, "so a request to connect an account feels routine." Invitation emails that send victims to these pages have been documented by IRONSCALES and Intezer, the researchers added.
The technique behind the Connect button is known as browser-in-the-browser. Instead of opening Google, the page draws a second Chrome window inside itself, with a lock icon and an address bar reading accounts.google.com, while the real address bar still shows the phishing domain. BleepingComputer, reporting on the research, noted that the method was devised by a security researcher in March 2022 and that the fake window is an iframe. Island said the kit adapts to Windows, macOS, iOS and Android, and newer builds copy small details such as Safari's URL pill, Chrome's custom tabs and dark mode. One comment left in the code explains that without a frosted toolbar effect, "the chrome looks painted-on and gives away the fake."
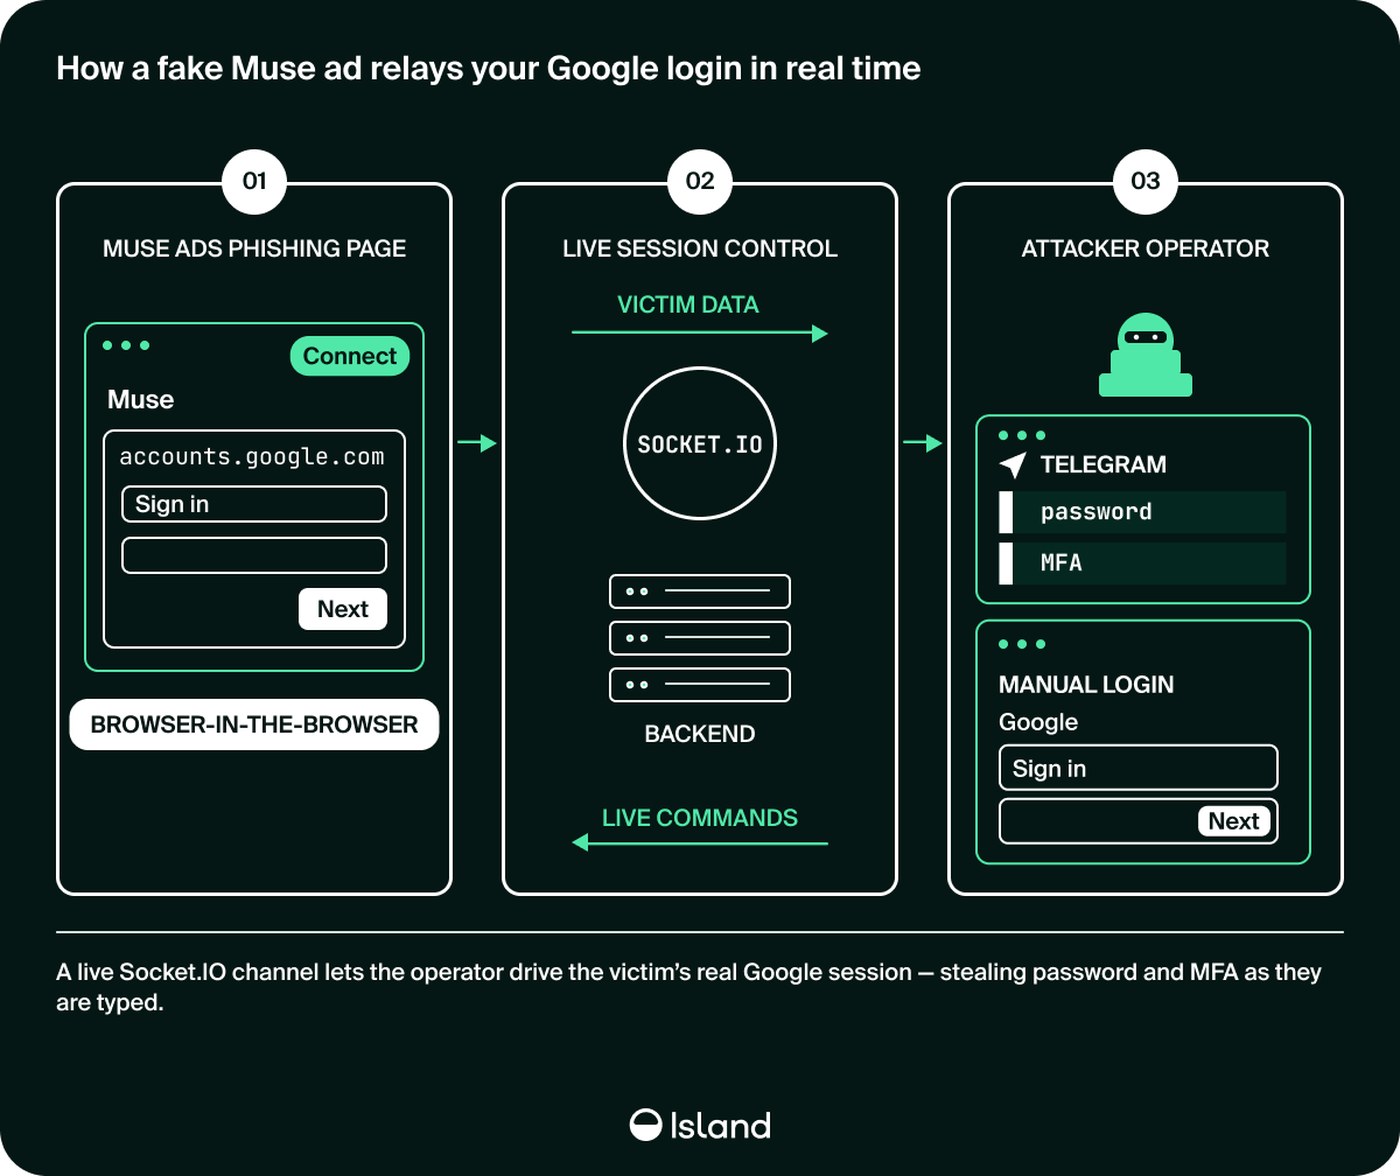
The window is only the presentation layer. When a visitor clicks Connect, the page creates a record through an endpoint at /api/create/user, fingerprints the device from IP address and location down to screen size and WebGL, and sends that profile to /api/send/ip, Island said. The platform stores up to three separate password attempts, so an operator can reject an entry, ask the victim to try again and keep every value. Commands arrive over Socket.IO events named operator-command and telegram-command, with a vocabulary that includes /2fa to request an SMS code, /authApp for an authenticator code, /googlePrompt and /oktaApprove for push approvals, /wrong2fa to reject a code, /done to finish and /ban to suppress the page for a visitor. Google, Meta, TikTok and Okta sign-in flows are supported. "Unlike a transparent reverse-proxy kit, the visible platform locally rebuilds the provider interface and collects credentials and MFA state through its own APIs," the researchers wrote. That makes the traffic look like an AI product talking to an unrelated application backend, not a session passing through a known identity-provider proxy.
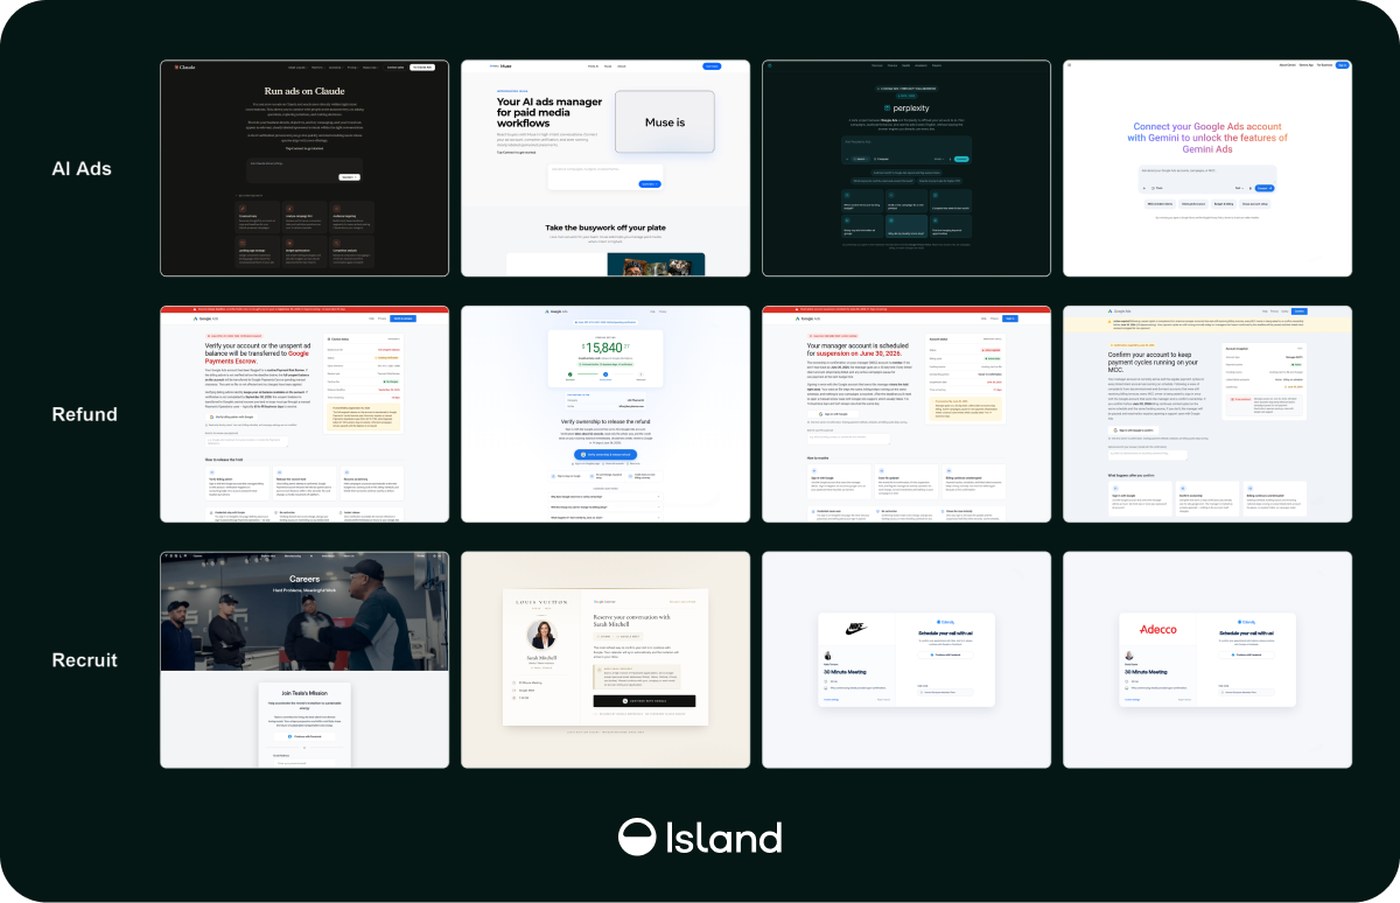
The same machinery serves more than advertising. Island said AI ad pages, refund claims and fake job sites all run on one Next.js and Socket.IO stack, calling the same endpoints, with many front ends hosted on Vercel and back ends on Railway or Render. One back end, backend-production-6d75.up.railway.app, appeared in 73 archived scans across 25 page domains between May 27 and June 20, serving Gemini, OpenAI and Anthropic ad lures as well as refund pages and a fake Louis Vuitton careers site. The operators exposed older versions of the platform's source code through misconfigured public GitHub repositories, Island said, including recruitment builds with Telegram wired in as the control channel. While tracking the campaign, the researchers saw hundreds of victim submissions, and the activity was still under way when they published. BleepingComputer cautioned that the submission count does not necessarily reflect the number of accounts successfully taken over.
The targets are chosen for what their accounts can spend. An advertising account carries a stored payment method and an approved budget, and a manager account can reach several client accounts, each with its own billing profile, Island said. Citing research by Mimecast, the report said attackers either run their own campaigns on a stolen account's budget or sell it, and that aged accounts with a clean spend history sell on Telegram for two to four times the price of new ones. Recovery is the hard part: attackers typically add their own administrators and downgrade the legitimate owner. The recruitment lures aim at a different prize, Island noted, because a job seeker may sign in with a work Google or Okta identity that opens a current employer's email, files and software-as-a-service apps.
Island sells an enterprise browser and closes its report by pitching it, but most of its guidance can be put to work without it. The researchers suggested correlating a client-side pattern that includes google_uid, repeated password fields, calls to api.ipify.org and ipapi.co, the /api/send/ip and /api/create/user paths, and Socket.IO connections to unrelated Railway or Render hosts, and hunting for the control vocabulary itself, such as add-user, update-user, operator-command and telegram-command, which they called more useful than commodity hosting addresses. They urged origin-bound passkeys and hardware-backed authentication, which remove the reusable password and one-time code this platform is built to collect. After any exposure, they said, teams should check every client account the identity could reach for new managers or partners, changed recovery details and campaigns or spending nobody approved. The report lists the ad, refund and recruitment domains tied to the operation. "A page can draw an address bar, lock icon, browser tab, QR prompt, or security dialog," Island wrote. "It cannot change the real browser origin."
Sources:
- Island: Behind the Connect Button: The Fake AI Ads Campaign (Island, Oleg Zaytsev and Ofek Ronen, Oct 6, 2026)
- BleepingComputer: Fake ChatGPT, Gemini Sites steal advertising accounts, MFA codes (BleepingComputer, Oct 6, 2026)
- The Hacker News: Fake ChatGPT, Gemini, and Claude Ad Portals Capture Credentials and MFA Codes (The Hacker News, Oct 6, 2026)
Priya Shah covers threat intelligence, intrusion analysis, and adversary tradecraft for SOCtember from Singapore.
Related stories
Detection
Microsoft Tracks EvilTokens Phishing Kit Behind Device Code Token Theft
Detection
Microsoft Warns ClickFix Lures Now Hide Their Payload in the Browser Cache
Threat Intel
ClingSTUN Backdoor Turns Unpatched IoT Devices Into Proxies Hidden in Public STUN Traffic
Threat Intel